
"Plugin4Shell": The Flaw That Broke Trust in Every Major AI Coding Agent's Plugin System
Four of the most widely used AI coding agents shared a hidden flaw that let a plugin you already trusted turn against you — with zero clicks required.
Security firm AIR disclosed a vulnerability called Plugin4Shell on September 17, and the mechanism behind it is worth understanding, not just the headline:
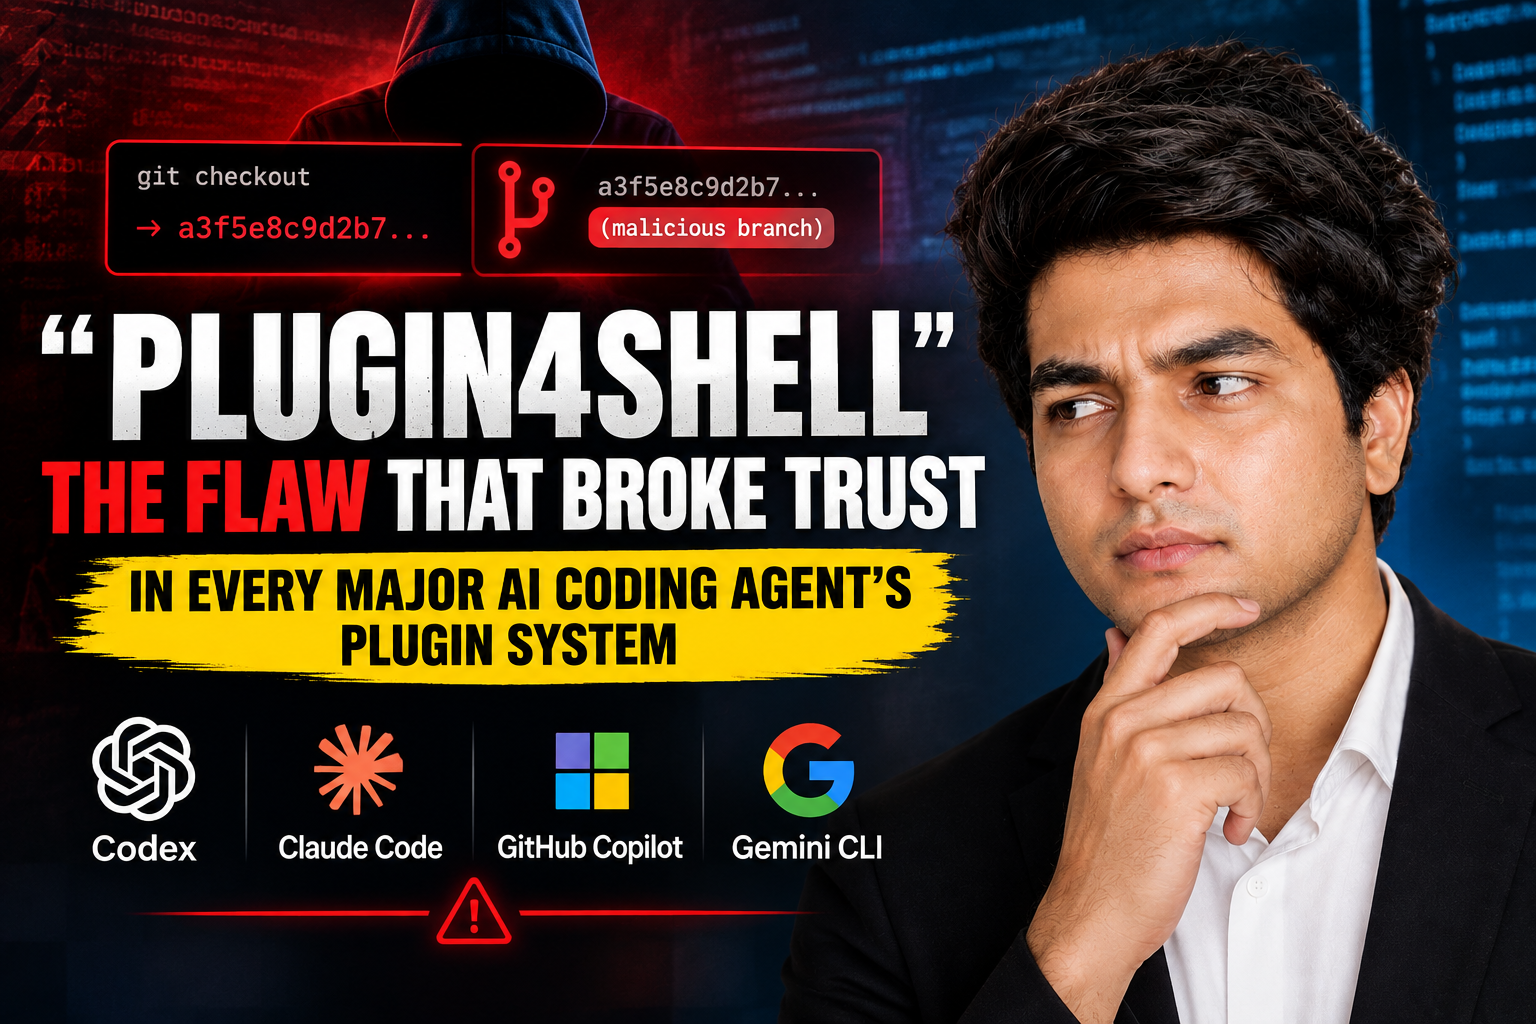
→ AI coding agents "pin" plugins to a specific, reviewed Git commit — a 40-character hash — as their core safety guarantee, promising you're always running exactly the code that was approved
→ Researchers found that if an attacker creates a branch whose name matches that commit hash, Git prefers the branch reference over the actual commit object at checkout — so the agent runs malicious code while still believing the pin was honored
→ Claude Code and Codex auto-update installed plugins in the background by default, which is what makes this zero-click: no new install, no prompt, nothing for the user to approve or even notice
→ The exposure isn't limited to careless users — you only need to already have a plugin installed from a marketplace you trust, reviewed and pinned exactly as the security model intended
→ AIR reported it to all four vendors in June. Three months later: Anthropic patched Claude Code (v2.1.179), OpenAI patched Codex (v0.146.0), Microsoft has shipped no fix for GitHub Copilot, and Google simply deprecated Gemini CLI rather than fixing it — leaving every existing install permanently exposed
→ No CVE has been assigned, and no in-the-wild exploitation has been confirmed yet, but working proof-of-concept exploits exist against all four agents
Here's what makes this different from a typical patch-and-move-on vulnerability: it doesn't exploit a mistake anyone made. Developers did everything the security model asked — installed a reviewed plugin, from a trusted marketplace, pinned to an approved commit. The flaw lived in the assumption that "pinned" actually meant "verified," and it didn't. When two of four major vendors still haven't fixed it — one by choice, one by simply walking away from the product — that's not a story about one company's bug. It's a signal that AI agent supply chains are being built faster than they're being secured.
If you're running Claude Code or Codex, update now. If you're on Copilot or Gemini CLI, there is currently no patch — treat that as an active risk, not a future one.
#Cybersecurity #AICodingAgents #Plugin4Shell #SupplyChainSecurity #InfoSec #TechNews
— 𝔖𝔞𝔫𝔡𝔢𝔢𝔭 ℜ𝔞𝔦𝔷𝔞