
IDScan Breach: Over 150 Million Driver's Licenses Stolen — Including One Belonging to the US Defense Secretary
An identity-verification vendor most people have never heard of just confirmed one of the largest ID-document breaches on record — and it sat undetected for over a year.
IDScan.net, a Louisiana-based company used to verify government IDs at bars, car rental counters, cannabis dispensaries, and shipping pickups, confirmed hackers stole data from its cloud environment.
Here's what makes this one different from the usual breach headline:
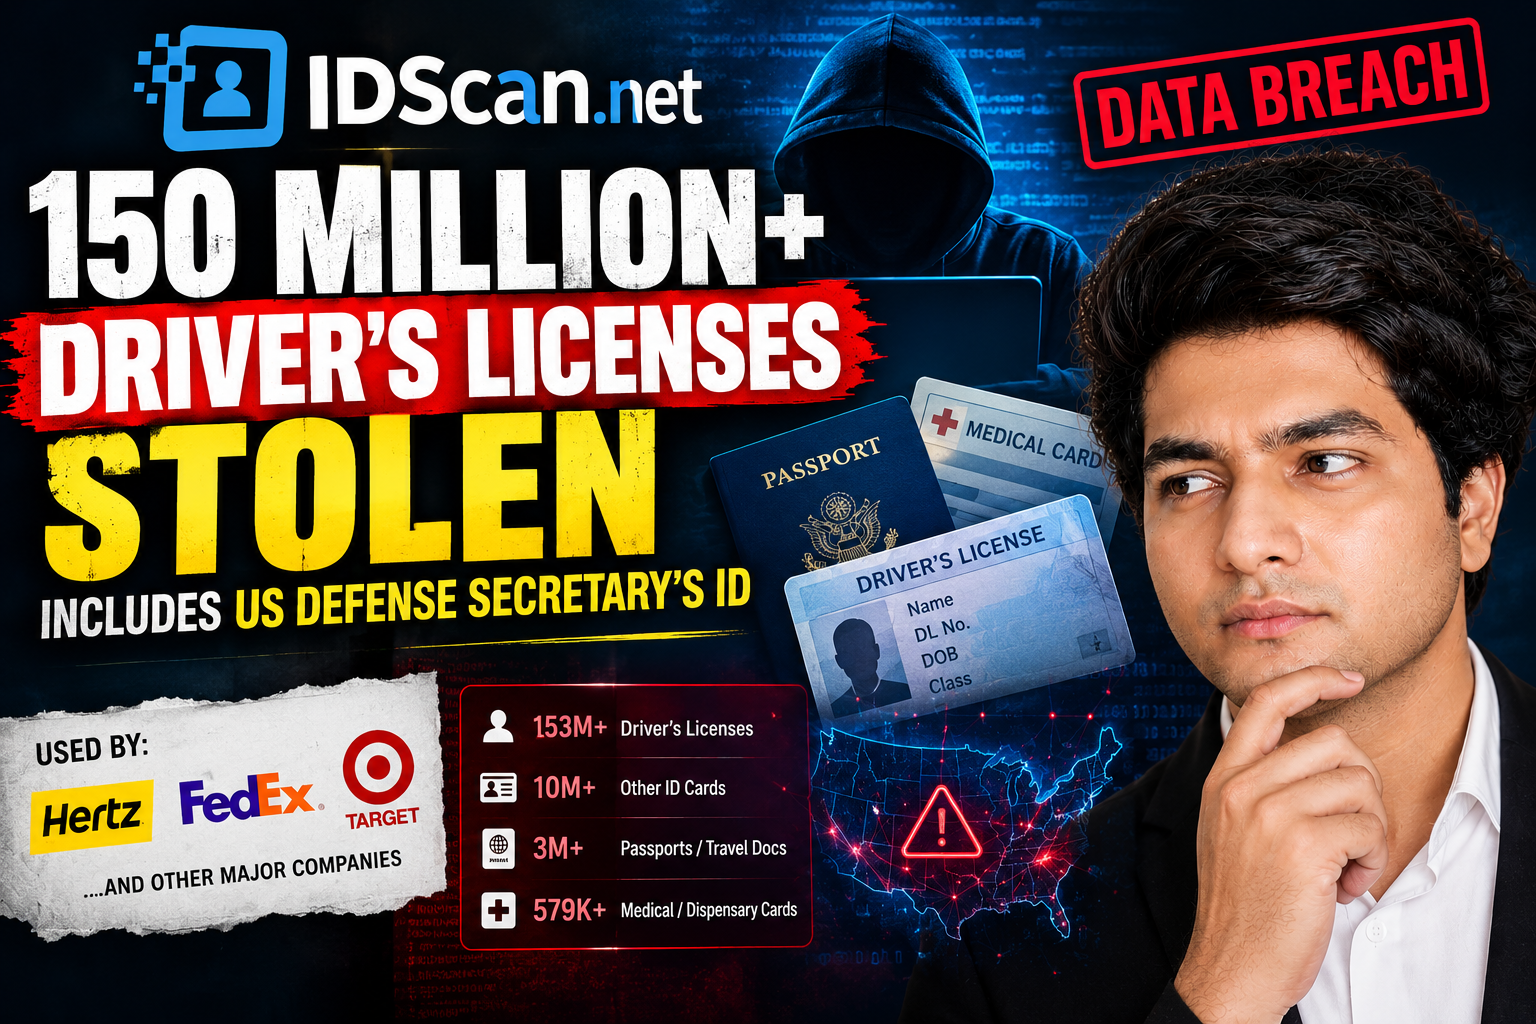
→ A dark-web marketplace called Nexus was selling the trove, initially claiming 153+ million driver's licenses, plus ~10 million other ID cards, 3 million passports/travel documents, and even 579,000 medical/dispensary cards
→ The stolen data includes full names and driver's license numbers — along with ID numbers from passports and other government documents
→ The seller told researcher Brian Krebs the data had been "continuously exfiltrating for over a year," with nearly 400,000 new records added in a single 24-hour window — this wasn't a one-time smash-and-grab, it was an active, ongoing pipeline
→ Records reportedly found on the marketplace included IDs belonging to the US Defense Secretary and an FBI assistant director
→ IDScan.net's enterprise client list reportedly includes companies like Hertz, FedEx, and Target — meaning the exposure likely touches people who never directly interacted with IDScan at all
→ The FBI is now investigating alongside the company
Here's what stands out to me: this breach didn't happen at a company you chose to trust. It happened at a vendor working quietly behind the businesses you did trust — the rental counter, the delivery pickup, the age-verification scan. That's the uncomfortable part of identity verification infrastructure: your ID gets copied into systems you never see, run by companies you never agreed to use, and you only find out something went wrong when a dark-web listing does the disclosing before the company does.
If a year-long, active exfiltration can run undetected at a vendor serving companies of this size, the real question isn't just "how do we patch this hole" — it's how many other ID-verification pipelines are quietly leaking right now, un-discovered.
Have you ever stopped to think about where your ID actually goes when you hand it over to "verify" something?
#DataBreach #Cybersecurity #IdentityTheft #DataPrivacy #InfoSec #TechNews
— 𝔖𝔞𝔫𝔡𝔢𝔢𝔭 ℜ𝔞𝔦𝔷𝔞