
Hackers Didn’t Steal Anything From French Supermarkets. They Just Turned the Fridges Into Ovens.
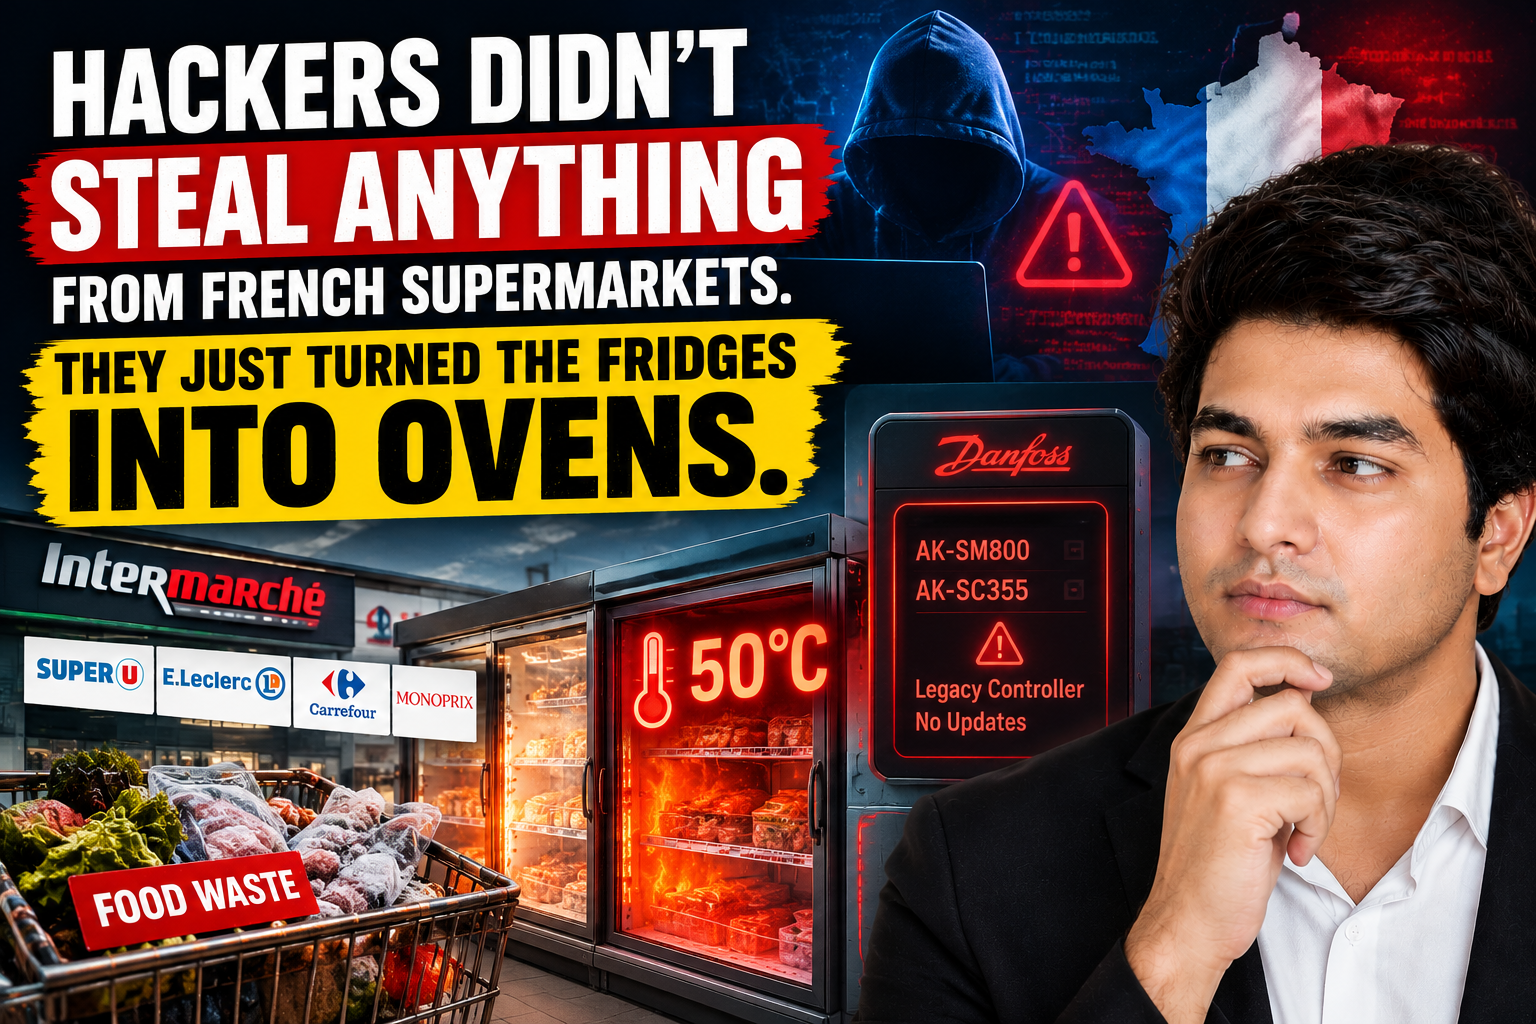
Overnight between October 11 and 12, attackers took control of refrigeration systems at hundreds of French supermarkets and pushed fridges and freezers up to 50°C. By Monday morning, stores were throwing out meat, vegetables, and frozen goods.
 Here’s what’s confirmed so far:
→ Intermarché, Netto, Coopérative U (Super U/Hyper U), and E.Leclerc were hit, with Carrefour and Monoprix reportedly affected. Early counts range from about 150 stores for Intermarché alone to 250-350 across all chains
→ The attackers reportedly forced a remote defrost cycle on Danfoss refrigeration controllers. Intermarché’s parent group says temperatures stayed near 50°C for around six hours
→ Danfoss says most of the affected equipment is legacy, including its AK-SM800 and AK-SC355 controllers, which no longer receive software or security updates. Leclerc says it had long advised stores to move off those models
→ The Paris prosecutor has opened an investigation into the “large-scale cyberattack”
→ Coopérative U’s CEO called it “unprecedented,” saying that targeting equipment essential to preserving fresh food and the national food supply is extremely serious
One detail makes this more uncomfortable. In August, Claroty’s Team82 researchers flagged a hidden login mechanism in Danfoss controllers, based on a daily code, that could give an attacker admin access. Danfoss released a firmware fix. But neither the retailers nor Danfoss have said how the attackers got in, so any link between that flaw and this attack is unconfirmed.
Here’s what stands out to me: this attack stole no data and demanded no ransom that we know of. A French retail news site described it as an attack that “steals nothing, but destroys everything.” That is a different kind of cyber risk from the breaches most companies plan for. The damage is physical, immediate, and measured in spoiled inventory rather than leaked records.
It also exposes a gap that has nothing to do with AI or cutting-edge exploits. Old industrial controllers keep running long after the vendor stops patching them, often connected to networks that were never designed with attackers in mind. Replacing them is expensive and easy to postpone, right up until the day the bill arrives as a store full of ruined food.
If a controller in your own business or supply chain stopped getting security updates years ago, who would know, and who would own the decision to replace it?
#Cybersecurity #CriticalInfrastructure #OTSecurity #SupplyChain #TechNews #Resilience
— 𝔖𝔞𝔫𝔡𝔢𝔢𝔭 ℜ𝔞𝔦𝔷𝔞