
Dell Patches 18 Critical Flaws — Including Two Perfect-10 Bugs That Could Hand Over Full Storage Admin Access With Zero Login Required
If your enterprise runs Dell storage on Kubernetes, this is the kind of patch that doesn’t wait for your next maintenance window.
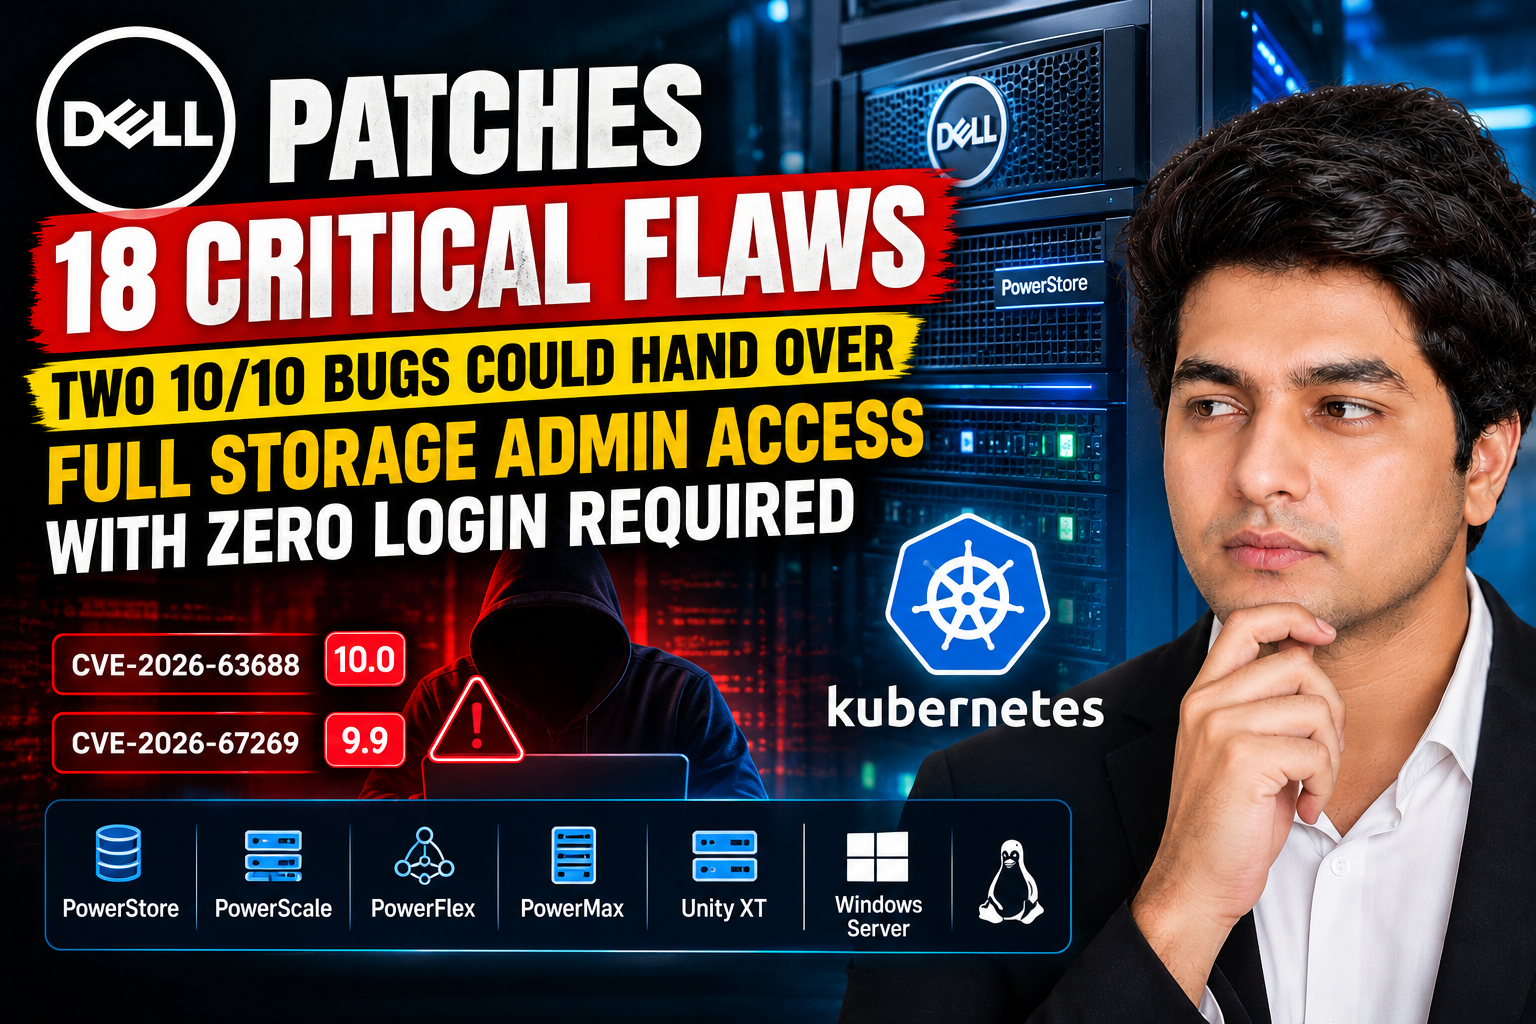
On October 1, Dell disclosed 18 critical vulnerabilities across two products: Container Storage Modules (CSM), which connects Dell’s enterprise storage arrays to Kubernetes environments, and Dell System Update (DSU), used to manage PowerEdge servers.
 Here’s what makes this one serious rather than routine:
→ Two flaws scored a perfect 10.0 on the CVSS severity scale — CVE-2026-63688 lets an unauthenticated attacker steal backend storage administrator credentials across all five supported Dell storage families (PowerStore, PowerScale, PowerFlex, PowerMax, Unity XT), handing them full admin control with no login required
→ CVE-2026-67269 (rated 9.9) lets a low-privileged attacker take root access over every node in an entire Kubernetes cluster through a single malicious resource submission — one bad request, whole cluster compromised
→ CVE-2026-54472 and CVE-2026-61421 (both 9.8) involve hard-coded credentials and forgeable authentication tokens that let attackers mint their own admin access
→ CVE-2026-67273 (9.6) bypasses Kubernetes access controls entirely, exposing cluster-wide read access to Kubernetes Secrets — the vault most organizations use to store their most sensitive credentials and keys
→ A separate 9.6-rated flaw in Dell System Update allows remote code execution with root privileges directly on PowerEdge servers
→ Dell says it has no evidence of active exploitation yet, but security researchers are already warning that proof-of-concept exploit code could surface within hours to days of public disclosure
The fix: upgrade CSM to version 1.18.0+ and DSU to 2.3.0.0+ immediately — and for the forged-token flaw specifically, Dell is telling admins to rotate their JWT signing secrets after patching, not just install the update.
What stands out here isn’t just the severity scores — it’s where these flaws sit. CSM is the connective tissue between your storage hardware and the Kubernetes clusters running your actual workloads. A flaw there doesn’t just expose one system; it exposes the layer that’s supposed to enforce boundaries between every tenant and workload running on top of it. When the access-control layer itself is the vulnerability, every assumption built on top of it needs re-checking.
If you run Dell storage on Kubernetes or OpenShift, patching this isn’t optional — it’s this week’s top priority.
#Cybersecurity #Dell #Kubernetes #InfoSec #CVE #EnterpriseSecurity #DataSecurity
— 𝔖𝔞𝔫𝔡𝔢𝔢𝔭 ℜ𝔞𝔦𝔷𝔞