

Hello guys hope you well , First of all Am Praveenarsh, a security researcher ,a part time hunter and a Space Researcher .
Buy me Coffee: https://buymeacoffee.com/praveenarsh0xx0
Am in more than a year in Bug bounty and penetration testings , but This is my first blog about to make a tricks in bug bounty :)
Ok lets start ..This is a small fuzzing technique to bypass using language server , ok we all know that for ex: we can translate a netherland language to english (like nl-en to us-en) in the URL like (www.target.com/en-us)behind the scenario there a particular server for each languages (some companies do )
Let’s say the vulnerable site name is target.com and this target is using a ./git folder , whenever i access the the www.target.com/.git/config/ it will blocked as 403. haa ok lets resaearch about language servers.
After some researches ,…..
Ok lets Bypass this , I suddenly open my kali and open FUZZ tool lets fuzz with the URL like ffuf -u http://target.com/FUFF/.git/config -w /wordlist.txt
Waiting…………………….
After couple of minutes i got 200 ok with the URL https://target.com/fr/.git/config , and successfully accessed .
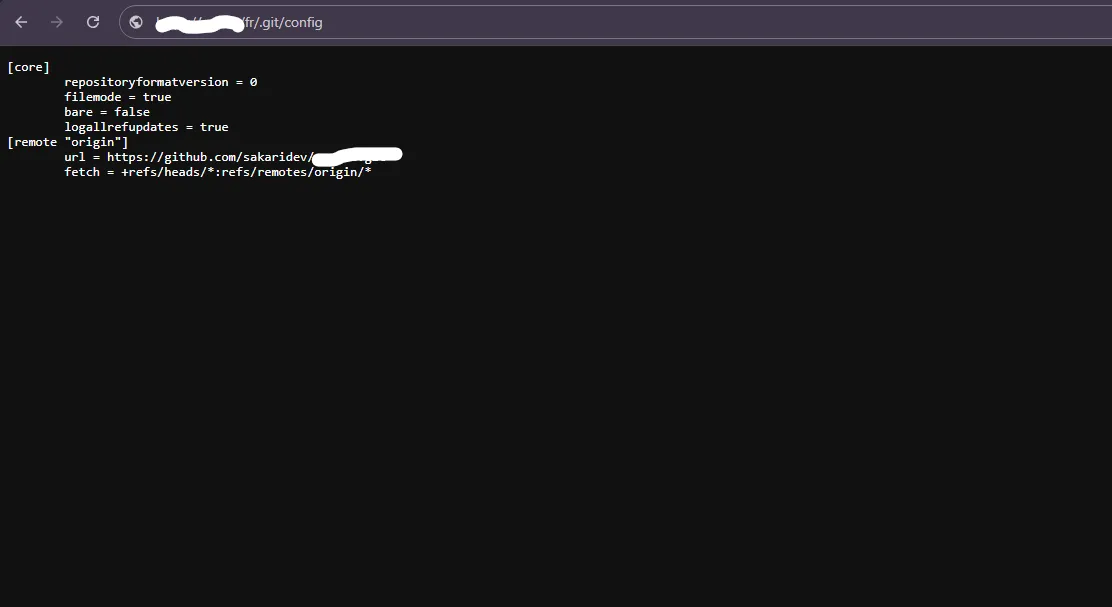
Whenever I use a language path(like ““/fr ,”) , it will allow me to access the sensitive content.
Conclusion:
Don’t ignore the domains which have a language changer , not all security configurations done on all the language servers.
Submitted: 25 /04/2024
Triaged : 29/ 04/2024
And we got a bounty with 200$