

TeamPCP (also known as PCPcat, ShellForce, or DeadCatx3) is a financially motivated cybercriminal group active since late 2025, specializing in large-scale, automated cloud-native infrastructure compromises and supply chain attacks. As of May 2026, they are considered a major threat, having compromised over 500,000 machines and numerous, widely-used open-source tools to steal developer and cloud credentials.
Hi, thanks for taking your time speaking with me. For everyone who might not be that deep in cybercrime - who is TeamPCP, and what do you do?
We exist as a loose team of malware developers and "cloud native" threat actors for a lack of a better word, our main objective initially was to farm as many credentials as possible using worm like malware to get our hands on data.
The first campaign publicly linked to this team alias was PCPcat which served that purpose and is a good example but definitely not our best or even most successful work prior to these supply chain attacks, it was rushed out to hit react shell before it was patched.
PCPcat exploited React2Shell (CVE-2025-55182) in December 2025 to compromise over 59,000 servers in under 48 hours, harvesting cloud credentials, SSH keys, and .env files at industrial scale.
That being said the core group have all been writing similar malware for a years now separately from one another and I would consider anyone who introduces tradecraft to us and collaborates/furthers the ops we're involved in, in a positive way, a part of the team.
There isn't any strict leadership structure, but I solely represent the alias so I am known as the "leader". This structure is good, it means arrests do not cause any major disruptions and the aliases can just pass on.
PCP is a dissociative drug, a hallucinogen. Why did you choose that name?
A lot of people here are recovering addicts and ex vendors/dealers, cyber crime is their therapy in a weird way, it keeps them sober, it distracts them from their shitty situations, let's them escape for a while doing something purposeful they're good at especially when they don't have the qualifications to do it legally. There is a component to this when you start dumping loot after a successful op where you get a huge rush, it's addictive.
That being said no one here encourages anyone tries or uses these substances we reference in our names, there was also a few of us who appreciated the work of another group by the name of TeamTNT and learnt tradecraft from their campaigns, so the name is also a tribute to them.
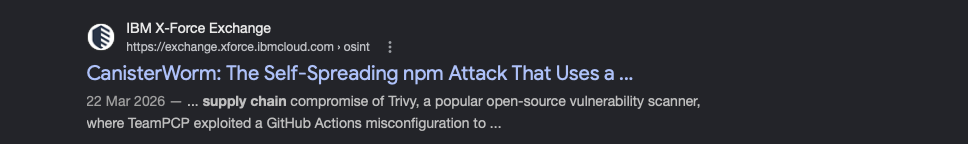 Security researchers called CanisterWorm the biggest supply chain attack of 2026. Some estimates say over 500,000 machines and 1,000+ SaaS environments were compromised.
Do you even know the full scope yourself?
I know the full scope yes but it's even difficult for me to comprehend, I think when I started sharing these credentials with the team and we saw all these fortune 500 companies, then another one then another one then another one, everyone sort of panicked and there was a race to dump data.
Thinking the credentials wouldn't last and involve other operators which was a mistake I will admit, it's difficult to teach 17+ people cloud exploitation and orchestrate something that large with good security and stealth, we are a lot more methodical with our approach now choosing not to involve third parties and taking it slowly.
This series of attacks may have been one of the most consequential supply chain security failures in recorded history and the sheer quantity of credentials are enough to overwhelm anyone.
And are there companies out there who are compromised right now and still have no idea?
Yes, if a company is still compromised they have 0 idea what's happening or how close we are to getting into their data warehouses/databases, and we are very strict about how we work to keep it this way.
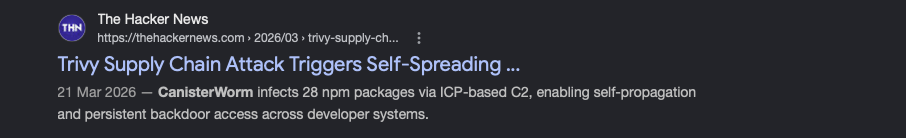 Let's talk about the supply chain.
Aqua Security and their vulnerability scanner Trivy was breached in late February by a separate, automated attack. You came in after, realised their credential rotation after the incident was done poorly, and you still had access. How did you find out the credentials survived?
This was shown to us by a good partner, I can't take credit for trivy/aquasecurity but I wont identify them either, they have been teaching us a lot of about git exploitation in the interest of involving us in these attacks to write/release effective malware, I would consider them a apart of the team, working with them has been an amazing learning experience and opened up a whole new frontier to us to replicate these attacks which you have seen downstream.
You used that access to inject malicious code directly into Trivy. The malicious code ran before the scan, but still let the scanner complete normally so everything looked clean.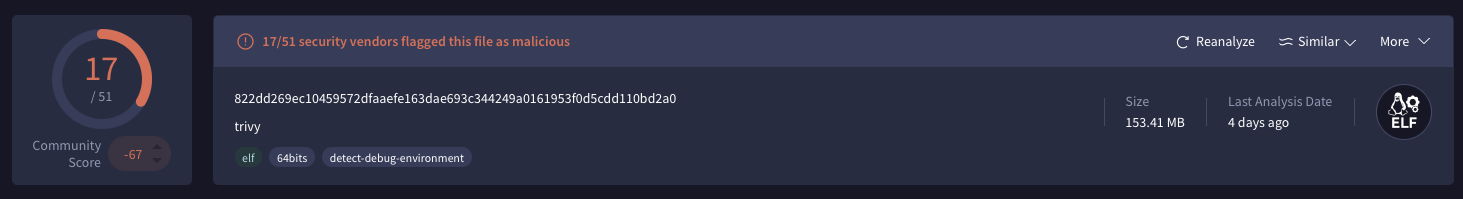 Researchers who analyzed it found a tool hardcoded in the code that called itself "TeamPCP Cloud stealer" - what does it do and does it bypass modern security solutions?
TeamPCP cloud stealer was a refactored version of the pcpcat stealer with an added runner memory parser script and hybrid encryption for the exfiltration, it's pretty basic malware, we just wanted something that worked initially, but now we are optimizing to steal as much as possible while we are on the developers machines from their different keys.
I don't know how many researchers looked into this too heavily, we also poisoned the trivy binary with a malicious checkout in the build/release workflow that compiled the tool with our code, this lead to a signed release being distributed which was probably a lot stealthier, we were going for more of a smash and grab with the poisoned actions and modified release tags.
From there you then pivoted to 66+ npm packages via CanisterWorm, Docker Hub images, then Checkmarx KICS and their VS Code extensions, then LiteLLM on PyPI, then Telnyx with payloads hidden in audio files, and eventually Bitwarden.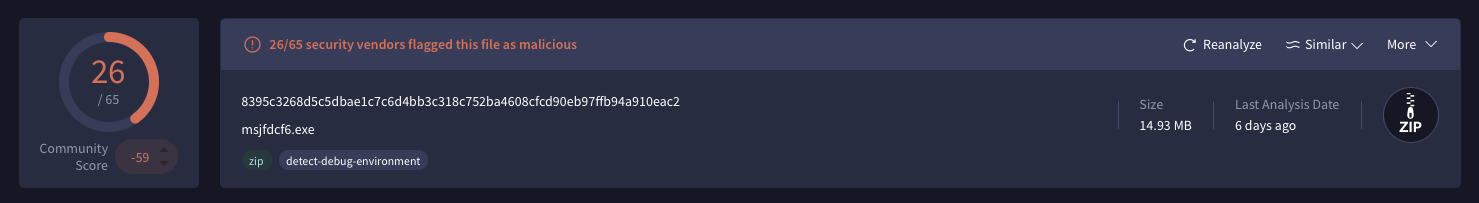 Was that the plan from the start, or did the chain just keep opening up as you went?
These types of attacks cascade between hundreds of thousands to millions of environments, there are transitive dependencies everywhere so it was expected but I didn't realize how big of an impact this would have downstream till we started validating credentials.
Now the potential snow ball effect is largely what we are chasing and we can position ourselves in the supply chain accordingly with the gathered credentials any ecosystem can be targeted and we often find credentials to move across from github to npm to pypi etc and using something like OIDC really doesn't protect anyone from this.
Researchers found that your Bitwarden payload (bw1.js) checks for Russian locales across three sources. Why?
People here come from all over the world. Some of us do not want the smoke from law enforcement, and it's largely avoidable with a few lines of code so anti CIS will be in place.
Researchers additionally found a GitHub account created three days before the Bitwarden attack, where someone was testing whether the C2 channel worked correctly before going live. How much preparation and testing goes into an operation like this before you actually pull the trigger?
It depends with the second wave of these we have spent ~1/2 a month waiting for the hype to cool down and experimenting with new malware and techniques before unleashing chaos. There is a lot of preparation and co-ordination between us but for the most part we are on the same page, and understand the end objective, which companies/tools are working against us and shoot ideas back and forth sometimes long before we even have a specific target in mind.
 CERT-EU also confirmed that the European Commission's AWS environment was breached through your compromised Trivy tool, with 340 GB of data stolen from 42 internal EU departments.
ShinyHunters then told TechCrunch they had taken some of that data and published it on their own leak site. What actually happened?
ShinyHunters saw our attacks and one of their members messaged a close friend asking them to sabotage our operation for money "I destroy any up and coming threat actor" (I still don't understand why).
They were in the Vect operator chat and a member asked to use the credentials, I said yes if they split the profit, so they downloaded them, then scammed us, refusing to pay releasing a mix of real and fabricated chats to try make us look stupid after being called out, these stolen credentials were how CERT-EU was breached, they downloaded S3 buckets from their AWS.
This was all a huge display of ego and shitty business practice, we were looking forward to collaborating but they just lied and scammed because they were jealous of the attention. That being said it taught us a good opsec lesson.
Perhaps you saw the CERT-EU announcement about the breach. An actor deployed TruffleHog and had AWS management rights over affiliated Commission accounts. The alerts fired 5 days later, when network traffic spiked during exfiltration. (https://archive.ph/iFKiF)
We didn't exfil from cert-eu at all, we don't even target gov and was operating more as an access broker at this point but after looking through the IOCs from the first campaign I realized very quickly that trufflehog was a huge red flag and same with the mullvad ips, one of the red teamers was even using boto3 on kali which is very bad opsec, so this is avoided as much as possible.
I won't describe the exact methodology but if we use this tool, it's with --no-verification and it operates offline, then we will move the keys to a clean environment where we can validate them manually.
Interviewers note: In this case it likely was ShinyHunters exploiting these techniques.
You have multiple groups working for and with you. I interviewed xploitrs before, and there is Vect. How did the collaboration with both xploitrs and Vect even come together in the first place?
Everyone in the scene know each other, whether they realize it or not, people I speak to daily surprise me, sometimes after months of chatting, revealing their aliases when enough trust is established, this leads to collaboration. Likewise I have worked with a lot of groups on joint operations without realizing it then stumbling into them later on.
 Vect 2.0 RaaS has a broken encryption - any file over 128 KB gets permanently destroyed because the decryption nonces overwrite each other. Victims who pay cannot get their files back.
I believe you are using a different, own locker for your operations instead?
I think the Vect operator is a very motivated person and will improve with time, this is a vetting fault and one of his maldev teams, but he will fix it.
Our collaboration has been for the red/negotiation team to process the credentials, We run our own proprietary locker, which currently 0 public samples exist of, I wrote this alone over the course of months and locked dozens of companies using and provided support unlocking systems, so I know it works, currently this exists only on encrypted drives locally, so anyone claiming to have my windows/linux malware is simply lying or possessing a fake copy.
Any leaks/vulnerabilities of vects tools or the s3 tools do not effect me and our partnership will end on good terms here.
How are you making money from all of this?
Vect never made us any money but I don't particularly like to sell data or do anything directly, once we've acquired data we will work through third parties to monetize always so this doesn't link directly back to us, the credentials will never be shared with said third parties though.
Cipherforce hasn't seen use in this campaign either it's a private tool, we hit atleast 15 companies with it the first month it was online separate to this, but for now I'm still deciding what to do with it, managing the platform and providing constant maintenance, bug fixes and feature updates is a pain, while also moving sometimes terrabytes of data around for ransoms, this ontop on my current activities it's just not viable, I only have so much time on my hands and 0 trust in anyone else possessing the codebase another thing I've noticed with modern day ransoms give the data is sensitive enough they don't even require encryption especially in cloud environments so it sort of seems pointless.
There are no arrests connected to TeamPCP, Vect, or xploitrs so far. Are you scared? Do you ever think about getting caught?
Any of these activities carry a huge life ending risk to them, we can never be too sure about who knows what about our members, I release a lot of fake intel and potentially identifying info to different groups to watch how the information flows to see who's talking to help mitigate this and I've seen some of this intel be weaponized and exchanged multiple times, which is funny.
We are learning very valuable opsec lessons as well about who we trust with inside knowledge of the group. I am very cautious, and if someone gave me an offensive security job where the goal wasn't to just test security but to steal data legally, I would 100% take it, it would fulfill the same itch.
Have you already identified leaks within your own circle from this campaign?
From the core group, there have been 0 leaks, they are extremely well vetted and very close friends, whenever people try to engage me though outside of that circle, then yes I've identified a few and will continue to.
You seemingly have a lot of technical understanding to execute supply chain attacks like this. Were you involved in known breaches before this, and how long ago did you start hacking?
This is pretty typical in this scene I gather, people start young with writing or skidding memory hacks for video games, that atleast was a major pivotal moment where I decided this was what I enjoyed, it got me onto a few forums where I learnt about cybercrime and spread a lot of my own spicy tools to test them, prior to that it was a more casual activity.
I started very young writing my first site in PHP at 9 and my first stealer, even if it was very basic and only targeted wallets, when I was 11-12 years old, I have been around a long time spreading malware and exploiting vulnerabilities at scale, just not publicly or in view of large forums on known aliases. I always knew I would be doing this and I've been involved in some notable breaches previously although not that I'd like to link to the group.
Is there anything nobody outside your circle knows yet; something you're willing to share?
I think I shared everything I am willing to here, otherwise it could compromise me, my team members or further operations.
And one final question: If you could give one final message to everyone - what would you say?
We do not target hospitals, we do not target small businesses, non profits, governments, if you are a small developer or startup we do not care about your credentials, you have nothing to worry about, we will never ransom you and we will never use your keys to cause you financial harm. If you are a multi billion dollar or large israeli company then we're gunning for you and we're not going to stop any time soon.