

xploitrs is a hacking collective known for their involvement in the CanisterWorm supply chain operation that compromised Trivy, LiteLLM and dozens of npm packages in March 2026. Other groups involved in this breach were TeamPCP and Vect.
Security companies estimate that over 500,000 machines and more than 1,000 SaaS environments were impacted. Hello, and thanks for taking your time to speak with Inside Darknet. Before we start, can you share who you are?
I am box turtl from xploitrs
And can you also tell us what xploitrs is and how it relates to TeamPCP? From the outside, the two names are always used together in reporting.
xploitrs is its own group, but we helped on the canister worm operation so i named myself canister turtl
Did xploitrs just form because of CanisterWorm, or did you have attacks before this as well? Or is that something you don't share
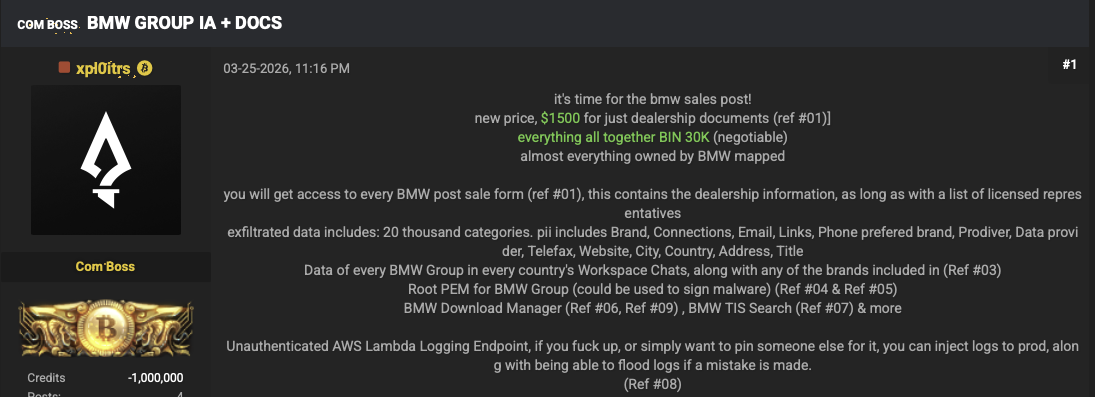
xploitrs has been a thing, we've also hacked BMW along with other car companies. we have much more to bring but the twitter has been banned so you havent heard much news on them
 For people who aren't aware what CanisterWorm and the operation behind is, can you share a little bit more?
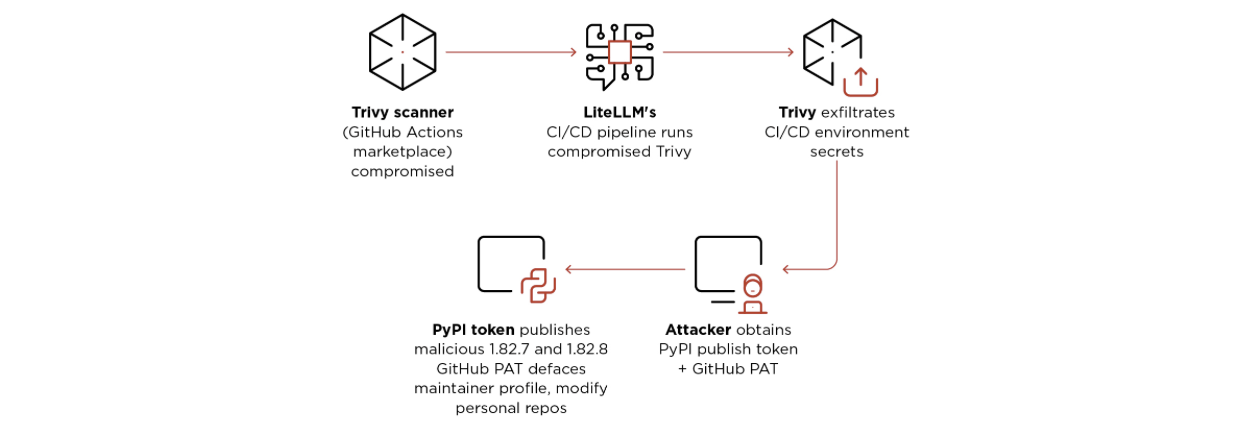
canister worm was the operation like trivy, checkmarx, litellm where teampcp spread its malware across the supply chain.
 I was unable to find any attribution of how you and your group were involved in the operation. Can you share a little bit more?
attribution even to xploitrs is hard to find even though it was mainly xploitrs and teampcp doing any work at all during the operation, i worked with others to validate, enumerate, and exfiltrate data.
And did you already work through all access, or will there be even more news to this supply chain attack?
more news ;)
 Attackers hijacked password manager Bitwarden’s CLI version 2026.4.0 through a compromised GitHub Action, publishing a malicious npm package that actively steals crypto wallet data and developer credentials.
Was the Bitwarden CLI your involvement too?
👍
You said "I am only participating in this operation for stories to tell my children one day xd". Is this true? Are you making money from this?
no, i make and have made no money from this nor have i asked the leader of teampcp for any.
You clearly have a deep understanding of various fields in hacking. How did you get into hacking?
it just happened, i met someone that modded on video games and got into it from there.
You mentioned that actual hacking is very different from CTFs. What are the biggest differences in your opinion?
simplicity, CTF's do not teach you about how idiotic people can be in practice, and then when they get sophisticated the chain is almost never something that could work.
Red Teaming would be much closer to what you do, I assume. Is this something you ever considered as a job?
I have, i do work professionally red teaming.
What types of systems or networks do you typically focus on when hacking? Is there a particular area you specialize in?
anything that needs exfiltrating, enumerating, authenticating.
Hacking often brings up ethical and legal questions. Are you ever concerned about the potential consequences?
to some extent yes but i think i have done a good job covering my paper trail. it used to be something that scared me but i cannot say that now with how incompetent every agency has been. no arrests have been made in connection with teampcp, vect, and xploitrs, nor anonymisations.
Can you share any memorable experiences or stories you've encountered?
Not outside of canisterworm but the insane amount of data we have (because some big places still have not rotated access) is insane. this one operation we've touched hundreds of billions of dollars worth of companies which was a fun time.
Was there anything super wild, or embarrassing badly secured that you saw in the campaign?
the bad thing was lack of organization and inclusion of idiots, personally i think vect should not have been involved.
You mentioned that the state of security after the AI wave is "horrible to look at." I very much agree with this of what I have seen in my red team engagements, but perhaps can you share why?
because looking inside of data, repositories things like this every big company is vibe-coding. horrible security and lazy engineers will be the death of computer science.
If you had one final message regarding cybersecurity and hacking, what would it be?
If you plan to go big, go big. dismantle corruption the conglomerates and governments support by hand if you need to.