
Hey everyone! 👋
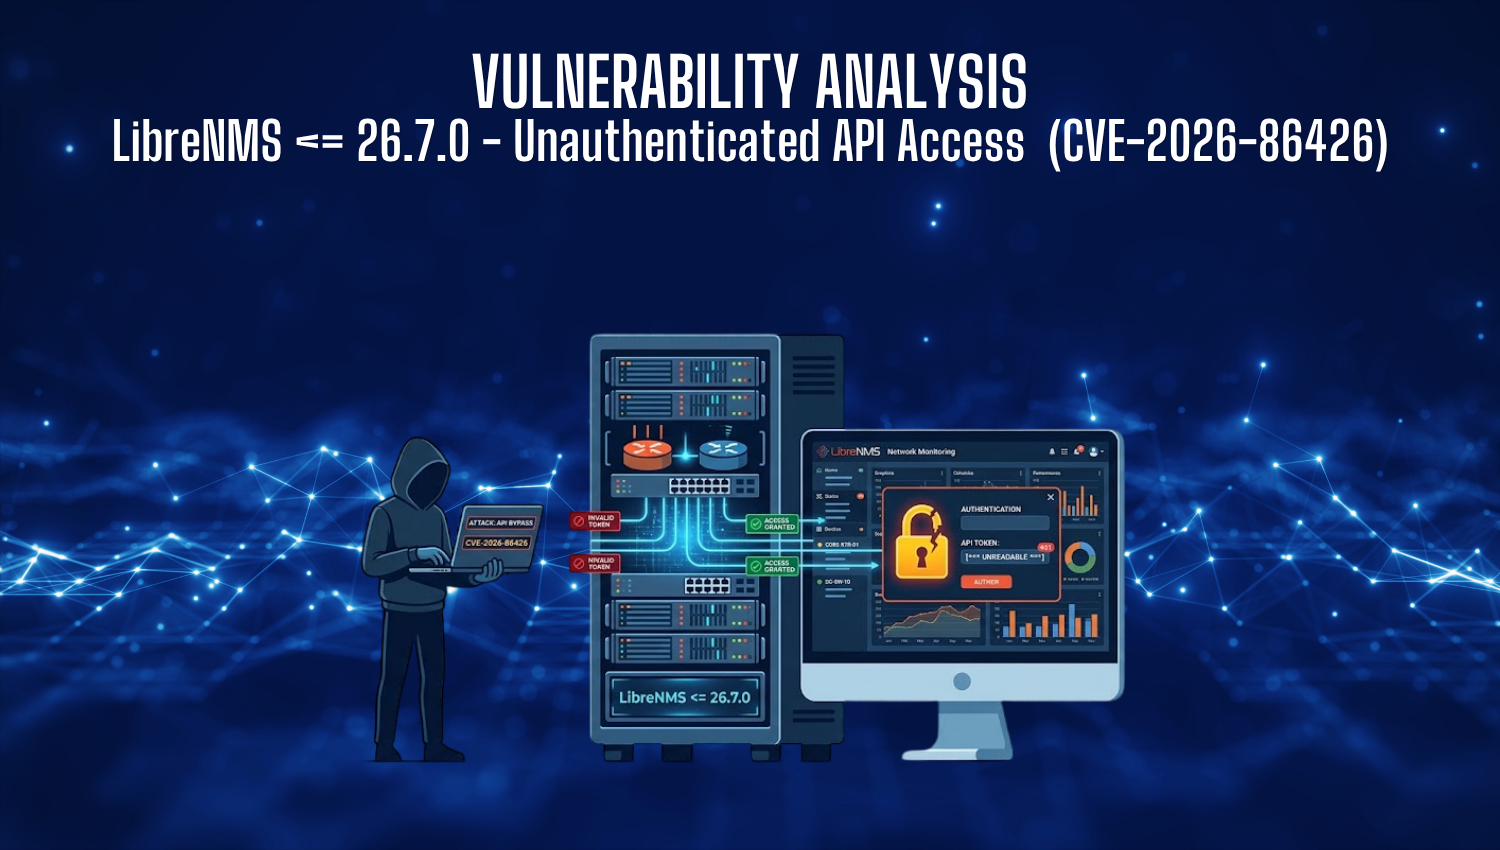
I just published a detailed security breakdown on a critical vulnerability that highlights how subtle interactions between web application frameworks and database engines can completely break authentication boundaries. Today, we’re looking at CVE-2026-86426, a severe authentication bypass flaw affecting LibreNMS versions <= 26.7.0 with a CVSS score of 9.2 (Critical).
What’s Happening Under the Hood?
The core issue lies within LibreNMS’s ApiTokenGuard middleware and how Laravel processes structured JSON payloads. When an API request is submitted as JSON, Laravel preserves native data primitives instead of casting everything to strings.
If an attacker sends a numeric payload like {"api_token": 0}, the integer primitive reaches MySQL directly. This triggers implicit type coercion:
MySQL casts string-based token hashes in the database into integers during comparisons.
Hashes starting with non-numeric characters evaluate to
0, while those starting with digits match their leading number.
Instead of guessing a high-entropy string, an unauthenticated attacker only needs to send single-digit integer requests (0–9) to hijack an active API session.
The Risk: Escalation to RCE
If the hijacked token belongs to an administrator, the attacker can leverage native administrative capabilities—such as custom PHP execution blocks (@php ... @endphp) inside alert templates—to gain full Remote Code Execution (RCE) on the host machine.
How to Fix It
Deployments running version 26.7.0 or lower must be updated to LibreNMS 26.8.0+ immediately to enforce strict parameter type checking.
☕ Read the Full Deep-Dive Analysis Thank you all for your continued support! You can read the full article featuring sequence diagrams, cURL exploit payloads, and step-by-step mitigation workflows over on my blog: