
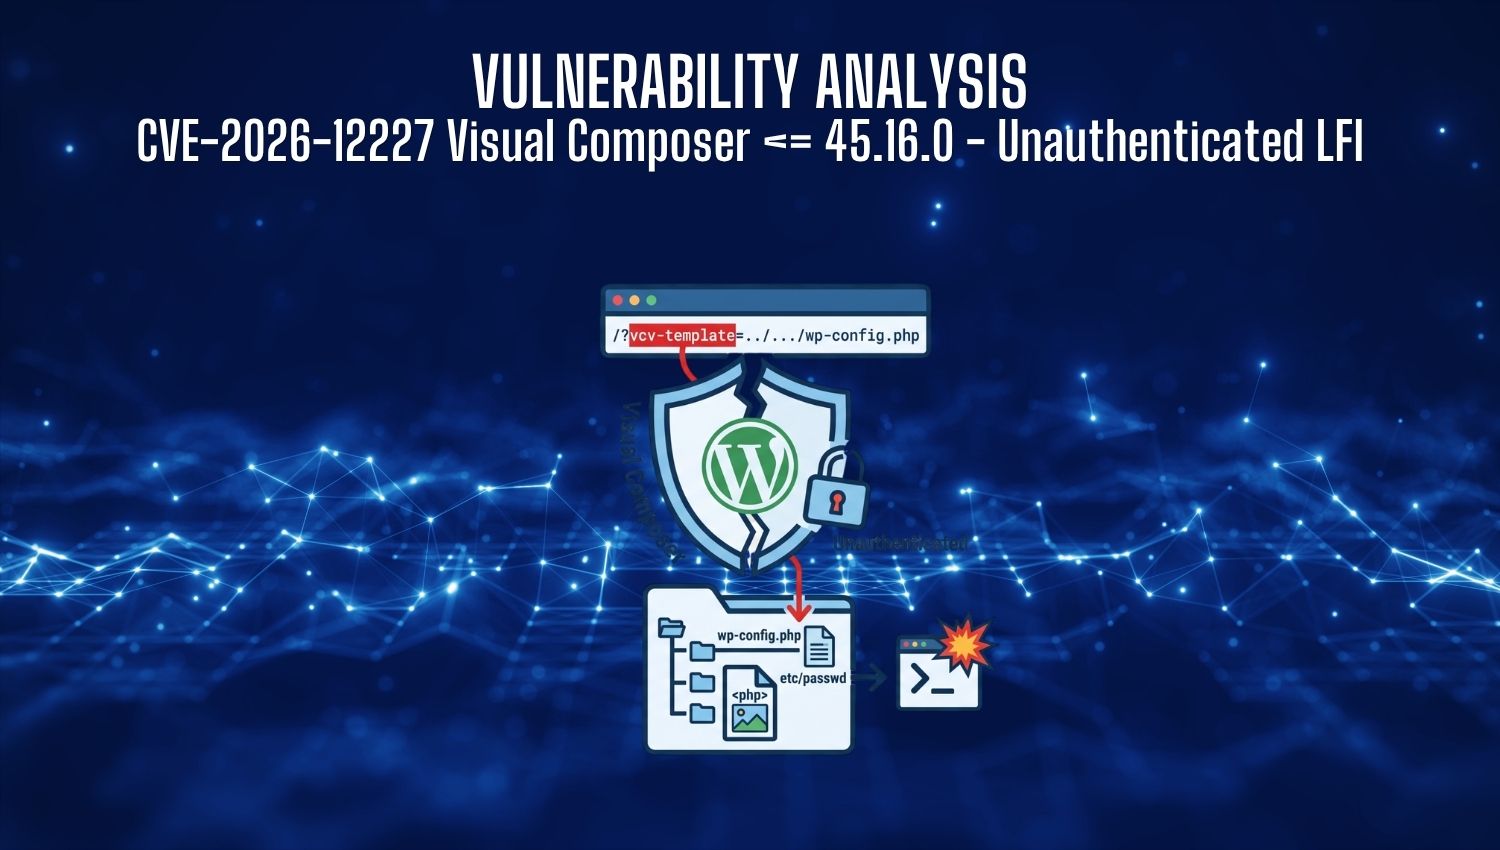
Hey everyone, thanks for the continued support! Grab your coffee, because we have a critical vulnerability to discuss today that affects one of the most widely used WordPress plugins on the market. If you or your clients are using the Visual Composer Website Builder plugin, it is time to take immediate action. A highly critical Unauthenticated Local File Inclusion (LFI) vulnerability has been discovered, tracked as CVE-2026-12227. Affecting all versions up to 45.16.0, this flaw boasts a CVSS v3.1 Base Score of 9.8.
The Anatomy of the Flaw
he vulnerability is rooted in the plugin's failure to properly sanitize the vcv-template parameter. Because this endpoint is completely unauthenticated, any malicious actor on the internet can interact with it. By injecting simple directory traversal sequences (like ../), an attacker can break out of the intended template folder and force the server to read arbitrary local files.
The immediate danger here is massive data exposure. Attackers can easily read sensitive configuration files like wp-config.php, stealing your database credentials in plain text.
The Escalation to RCE
However, the nightmare scenario for CVE-2026-12227 is its seamless escalation to Remote Code Execution (RCE). A savvy attacker doesn't just stop at reading files. By uploading a malicious PHP script disguised as a standard image file via the WordPress media uploader, they can use this LFI flaw to include and execute that hidden payload. This completely bypasses all authentication, giving the attacker full operational control over your server.
How to Protect Yourself
Patching immediately is non-negotiable. But to truly defend your infrastructure, you need to understand how these exploit chains work and how to implement defense-in-depth strategies like restricting PHP execution in upload directories.
I’ve put together a comprehensive, deep-dive analysis of this vulnerability, detailing the exact exploitation mechanics and step-by-step remediation strategies.
Read the full technical breakdown on my blog: 🔗 https://denizhalil.com/2026/09/29/vulnerability-analysis-cve-2026-12227-visual-composer-45-16-0-unauthenticated-lfi
Thank you for your support, stay secure, and keep patching!