
 After some time working quietly, I’m happy to finally release PayGOAT v2, a major update to my intentionally vulnerable banking platform designed for security learning, CTFs, and hands-on practice.
🏦 What is PayGOAT?
PayGOAT is a deliberately vulnerable banking application that simulates real-world business banking flows, including:
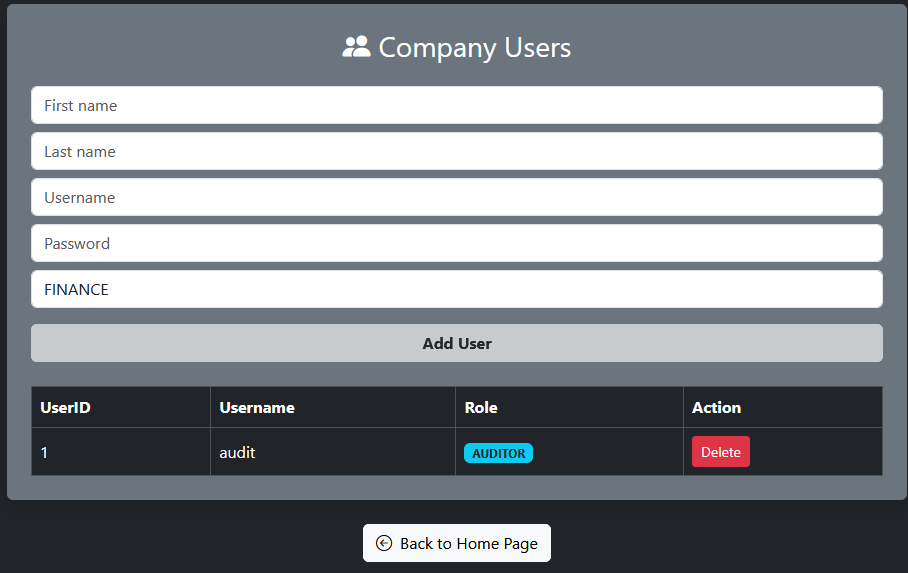
User and company accounts
Transfers and batch processing
Approval workflows
JWT-based authentication
SQLite backend
Clear frontend / backend separation
All built with security testing and exploitation in mind.
✨ What’s New in v2?
Empresarial Flow
CSV upload to generate batches automatically
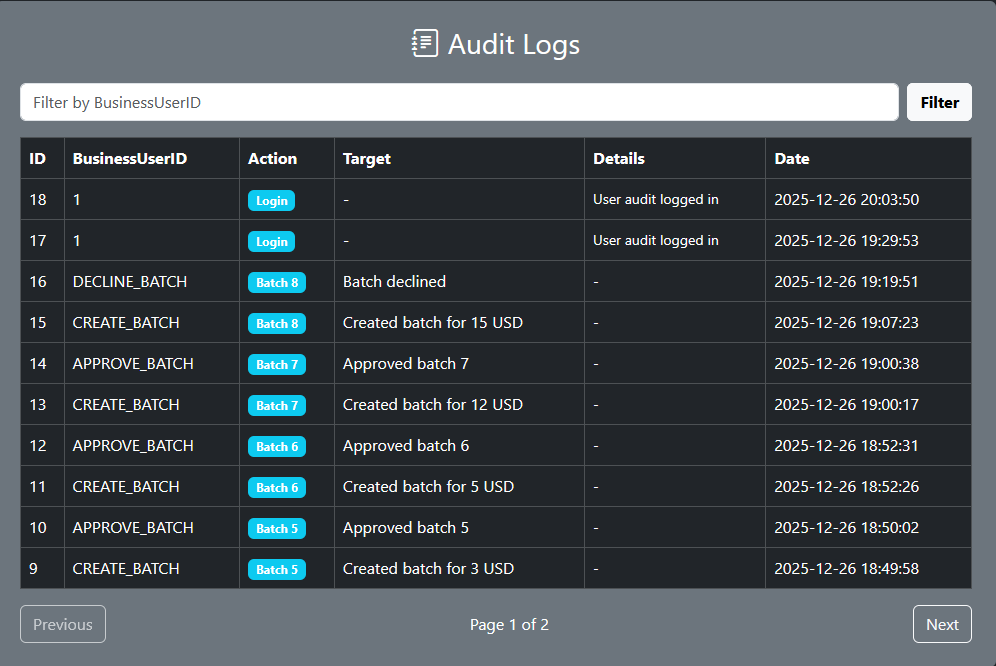
Approval / decline workflow
Realistic banking-style logic (and logic flaws 👀)
🔹 Role-Based Actions
FINANCEusers create batchesOWNERusers approve or declineClear role separation — and intentional gaps 😏
🔹 Intentional Business Logic Vulnerabilities
This version includes scenarios like:
Incorrect balance handling
Weak ownership validation
Authorization inconsistencies
Race condition–friendly flows
Batch ID handling issues
Perfect for logic-based exploitation, not just classic OWASP bugs.
Important Notes
This version may contain errors, inconsistencies, or weird behaviors and that’s part of the process
PayGOAT v2 is still being polished:
Some scenarios will be refined
Logic flaws will be adjusted or expanded
Code structure will improve over time
New vulnerable scenarios will be added gradually
Expect updates, fixes, and new challenges as the project evolves.
GitHub Repository
https://github.com/stuxctf/PAYGoat
Screenshots