
A Poem on GitHub Controlled a 3,400-Server Botnet, and Most Defenses Couldn’t See It
If you stumbled on this poem, you’d see two stanzas on a GitHub page. Nothing else. That’s exactly why it worked.
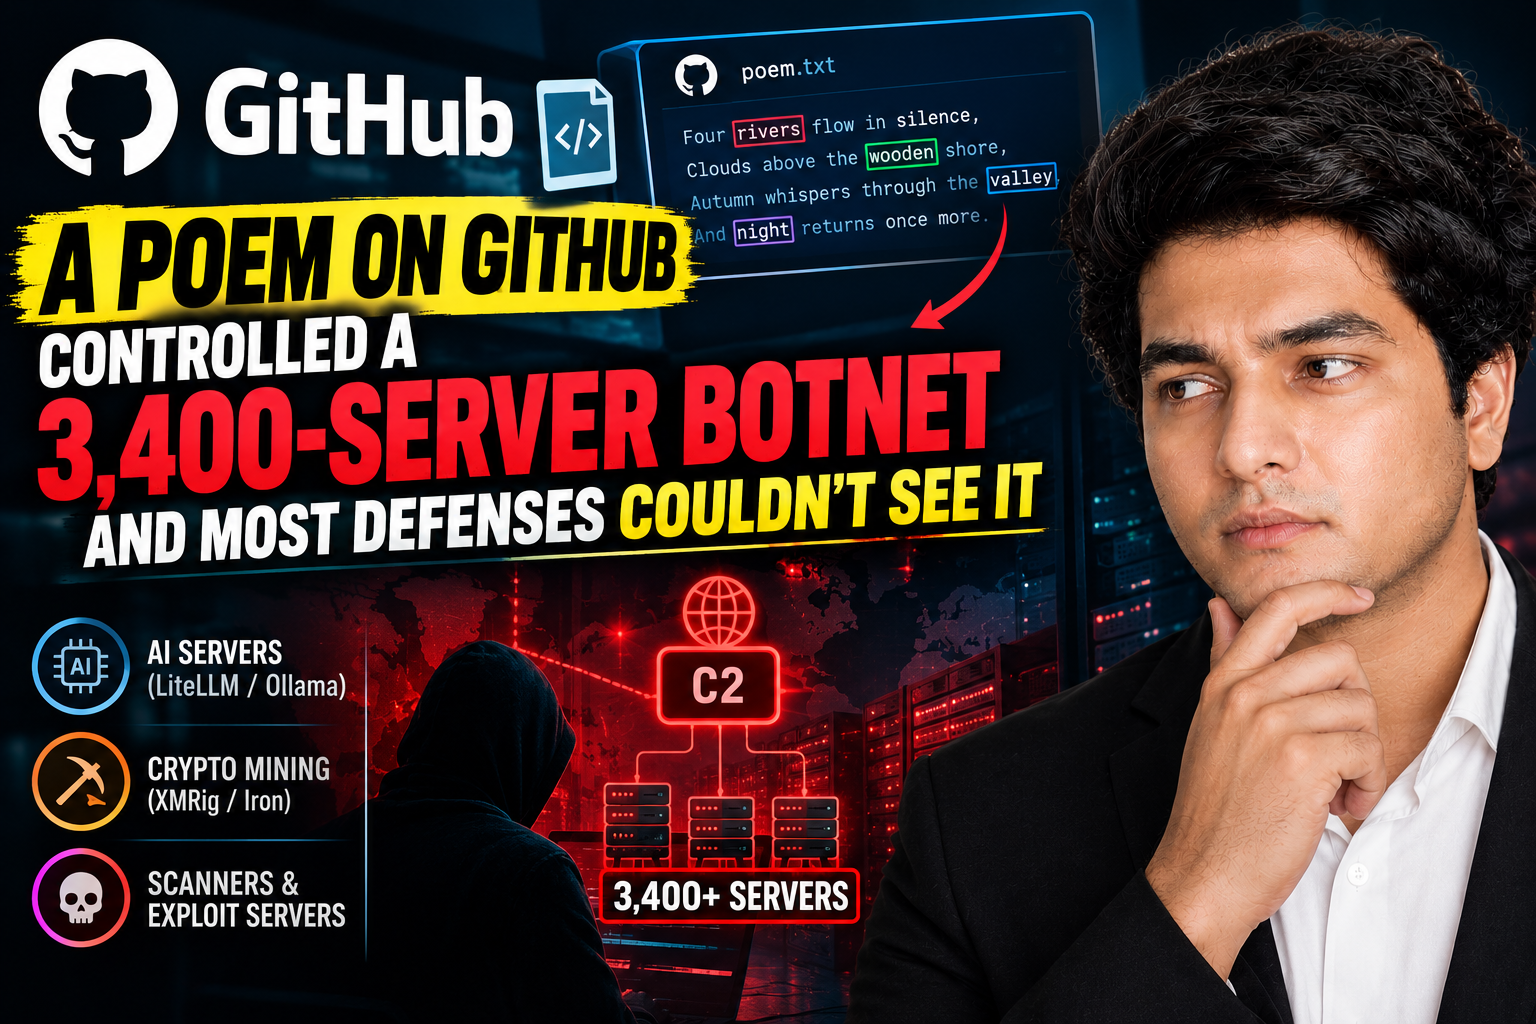
Lumen’s Black Lotus Labs disclosed a campaign it calls Canto Incognito. It’s powered by malware called PoeLLM, and it has compromised more than 3,400 servers since April 2026.
 Here’s the full picture:
→ The trick: the malware reads a poem hosted on GitHub, pulls four specific words or phrases from it, and converts them into the IP address of its command server. Swap a few words in the poem, and every infected machine gets rerouted without anyone touching the malware itself
→ The scale: nearly 800 servers were active on a single day at peak. The poem was edited at least 11 times, pointing the botnet to about a dozen different control servers
→ The targets: exposed AI infrastructure, mainly self-hosted tools like LiteLLM and Ollama, plus developer environments. Researchers say the campaign is unusual in going after multiple AI-related services
→ The payoff: cryptocurrency mining (XMRig and Iron miners), plus turning victims into scanners and exploit servers that hunt for the next vulnerable machine. One Lumen researcher described it as “a private army of AI-enabled proxies”
→ The attacker: Lumen attributes it, with moderate confidence, to an Italian-speaking operator, based on Italian comments in the malware and on the attacker’s GitHub pages, plus network traffic analysis. Researchers also believe the poem itself was AI-generated
→ The first: Lumen says it’s the first time it has seen “adversarial poetry” used in a real-world attack
One thing worth being precise about: here, the poem isn’t tricking an AI model. It’s hiding a control address in plain sight. That’s what makes it so hard to defend against. Blocking known IP addresses isn’t enough when the address changes with each poem edit, and the traffic to GitHub looks completely normal. Defenders have to rely on behavior, not static blocklists.
My takeaway is simpler than the poetry angle suggests: the entry point wasn’t clever. It was exposed AI servers with weak configuration and known vulnerabilities. The poem is the memorable part, but the real lesson is that a self-hosted LLM gateway deserves the same security discipline as any internet-facing production system. Many teams spin these tools up fast, expose them to test something, and forget them.
If your team runs LiteLLM, Ollama, or similar tools, this is a good week to check what’s reachable from the public internet and whether it’s patched.
When was the last time you audited which of your AI tools are exposed outside your network?
#Cybersecurity #AI #Malware #InfoSec #LLM #TechNews
— 𝔖𝔞𝔫𝔡𝔢𝔢𝔭 ℜ𝔞𝔦𝔷𝔞