
Windows 11 BitLocker Protections
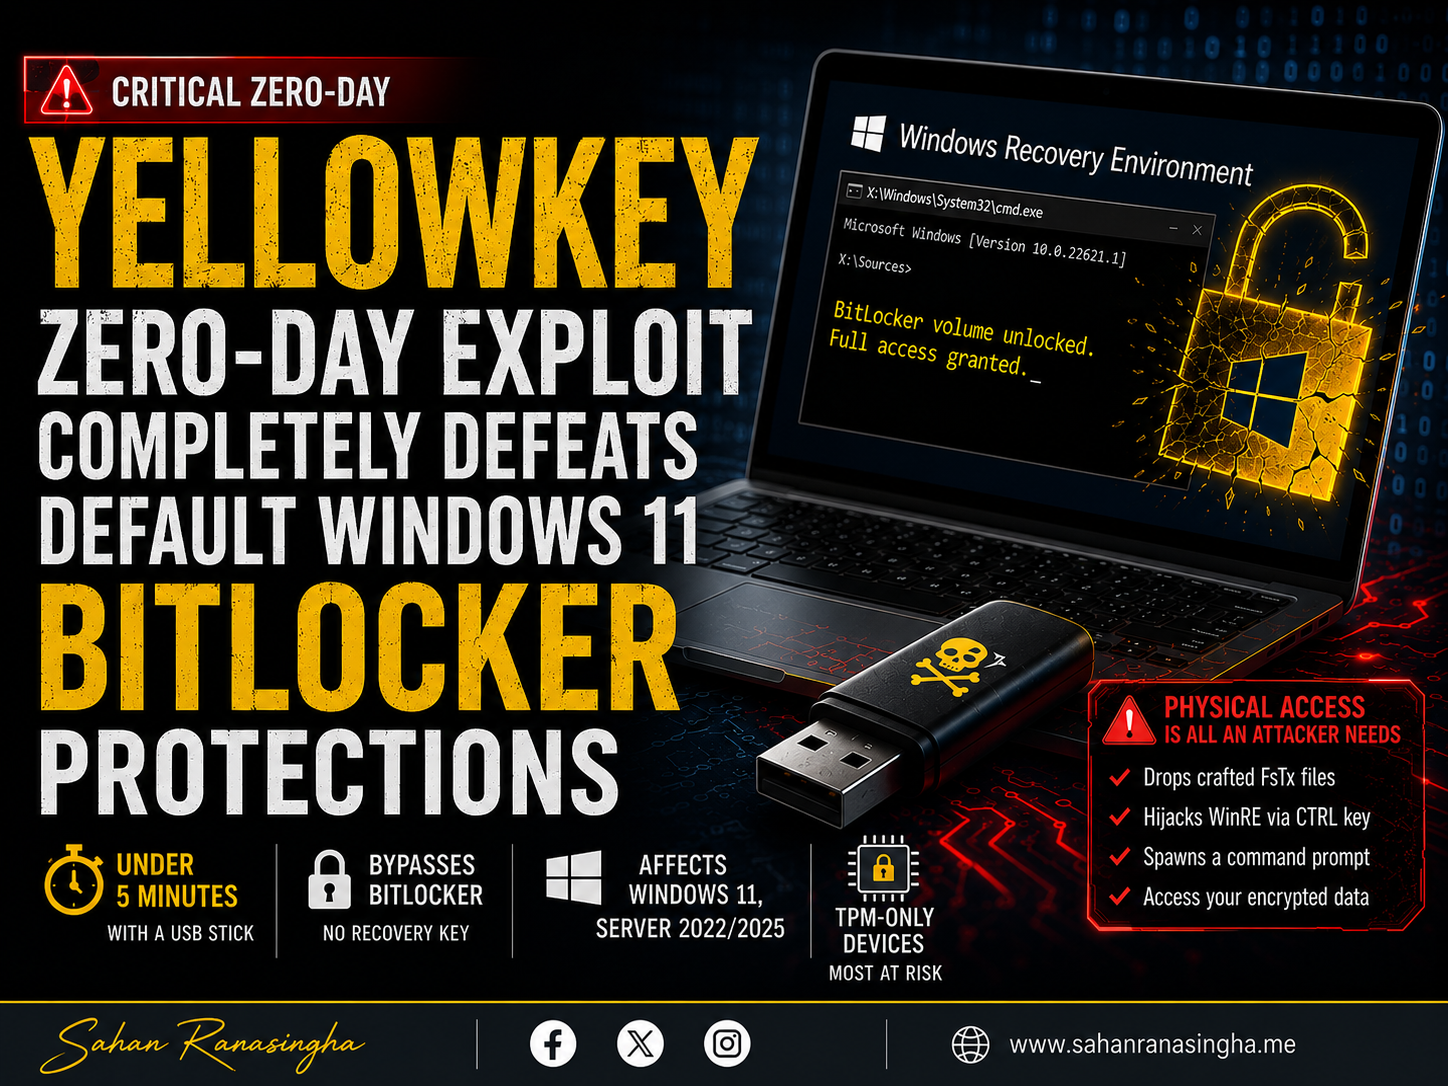
A critical vulnerability dubbed "YellowKey" has shattered the security of Microsoft's BitLocker encryption, allowing attackers with physical access to bypass protection in under five minutes using nothing more than a USB stick.
The Vulnerability That Shouldn't Exist
On May 12, 2026, security researcher known as "Chaotic Eclipse" (also operating under the alias "Nightmare-Eclipse") publicly released proof-of-concept exploit code for a newly disclosed Windows zero-day vulnerability called YellowKey that can bypass BitLocker encryption and expose data on protected drives without requiring the victim's recovery key. The disclosure has sent shockwaves through the cybersecurity community, as BitLocker is widely regarded as a last line of defense when a device falls into unauthorized hands.
What makes this vulnerability particularly alarming is its simplicity and effectiveness. The whole exploit resides in a folder you can copy to a USB stick, and the trigger is holding the CTRL key during a normal reboot into the Windows Recovery Environment. Multiple independent security researchers, including Kevin Beaumont, KevTheHermit, and Will Dormann, have confirmed the exploit works on recent Windows 11 builds.
How YellowKey Works
YellowKey exploits the trust Windows places in its own recovery environment (WinRE). The core mechanism involves dropping specially crafted NTFS transaction logs (FsTx files) onto a USB drive or directly onto the EFI partition.
The attack sequence is disturbingly straightforward:
Copy specially crafted "FsTx" files to a USB drive or the system's EFI partition
Plug the USB drive into a Windows 11 machine with BitLocker enabled
Reboot into Windows Recovery Environment (WinRE) by holding Shift while clicking Restart
Release Shift and immediately press and hold the CTRL key
A command prompt spawns with full access to the decrypted BitLocker volume
Security researcher Will Dormann noted that Transactional NTFS bits on a USB Drive are able to delete the winpeshl.ini file on another drive (X:), effectively hijacking the recovery environment's boot sequence.
Affected Systems and Scope
The vulnerability specifically targets:
Windows 11 (all current builds)
Windows Server 2022
Windows Server 2025
Notably, Windows 10 is not affected, raising questions about what changed in the Windows 11 recovery environment architecture.
The risk is most immediate for devices using TPM-only BitLocker, a common setup that automatically unlocks the operating system drive during startup. This is the default configuration on most consumer Windows 11 devices, prioritizing convenience over security.
The "Backdoor" Controversy
Perhaps the most explosive aspect of this disclosure is the researcher's assertion that the vulnerability may be an intentional backdoor. The researcher states that the component responsible for this bug is not present anywhere except inside the WinRE image, and what raises suspicions is the fact that the exact same component is also present with the exact same name in a normal Windows installation, but without the functionalities that trigger the BitLocker bypass issue.
Chaotic Eclipse bluntly stated: "I just can't come up with an explanation beside the fact that this was intentional".
The researcher further noted in a recent update: "I think it will take a while even for MSRC to find the real root cause of the issue. I just never managed to understand why this vulnerability is sooo well hidden".
TPM+PIN: Not the Silver Bullet Many Hoped
While initial advice suggested enabling BitLocker with TPM+PIN as a mitigation, the situation is more complex. The researcher claims that TPM+PIN does not help, stating the issue is still exploitable regardless, though they are not publishing the proof-of-concept for this version.
The researcher explained: "I asked myself this question, can it still work in a TPM+PIN environment? Yes it does, I'm just not publishing the PoC, I think what's out there is already bad enough".
However, some security researchers who tested the exploit have reported mixed results with TPM+PIN configurations, suggesting the bypass may depend on specific WinRE implementations.
A Pattern of Disclosure
YellowKey is not an isolated incident. The hacker first released the Windows Defender privilege escalation exploit on April 2nd, 2026, followed by another exploit on April 15th, both granting the highest (SYSTEM) privileges to attackers.
Previous exploits from the same researcher include:
BlueHammer (CVE-2026-33825) - A Windows Defender privilege escalation that security firms later linked to real-world intrusion activity
RedSun - Another privilege escalation flaw that Microsoft reportedly patched silently without an advisory
Chaotic Eclipse promised a "big surprise" for Microsoft, coinciding with the next Patch Tuesday release in June 2026, suggesting more vulnerabilities may be in the pipeline.
GreenPlasma: The Second Zero-Day
Alongside YellowKey, Chaotic Eclipse released a second exploit called "GreenPlasma." This targets the CTFMON (ctfmon.exe) process, which runs as SYSTEM in every interactive session and is responsible for text input features.
The researcher published a PoC exploit stripped of the code required to achieve a full System shell, explaining that it could be used to manipulate various Windows services, including kernel-mode drivers. The intentionally incomplete disclosure follows a capture-the-flag style, challenging other researchers to complete the exploit chain.
The combination of these two vulnerabilities is particularly dangerous: an attacker could use YellowKey to access an encrypted drive and chain GreenPlasma to escalate privileges within the same session.
Microsoft's Response (or Lack Thereof)
At the time of reporting, Microsoft has not issued a patch, assigned a CVE number, or released a public security advisory for YellowKey. The company provided a standard statement: "We also support coordinated vulnerability disclosure, a widely adopted industry practice that helps ensure issues are carefully investigated and addressed before public disclosure, supporting both customer protection and the security research community".
The researcher's decision to publicly disclose these vulnerabilities stems from alleged frustration with Microsoft's handling of previous security reports. In their blog post, Chaotic Eclipse sarcastically thanked "MORSE, MSTIC and Microsoft GHOST for making this public disclosure possible," naming three of Microsoft's internal security teams as the specific targets of the grievance.
The Bigger Picture: Related Vulnerabilities
The YellowKey disclosure comes amid other BitLocker-related security concerns. French cybersecurity company Intrinsec detailed an attack chain against BitLocker that leverages a boot manager downgrade by exploiting CVE-2025-48804 (CVSS score: 6.8) to bypass the encryption protection on fully patched Windows 11 systems in under five minutes.
These multiple attack vectors demonstrate that BitLocker's security model, particularly its reliance on the trusted boot chain and recovery environment, has fundamental architectural weaknesses that go beyond individual bugs.
Immediate Mitigation Strategies
While waiting for an official patch, organizations and individuals should consider these defensive measures:
1. Enable TPM+PIN Pre-Boot Authentication
Configure BitLocker to require a PIN before the TPM unseals encryption keys. While the researcher claims a bypass exists, the public exploit doesn't work against this configuration.
Implementation:
Open Group Policy Editor (gpr.msc)
Navigate to: Computer Configuration > Administrative Templates > Windows Components > BitLocker Drive Encryption > Operating System Drives
Enable "Require additional authentication at startup"
Set "Configure TPM startup PIN" to "Require startup PIN with TPM"
2. Implement BIOS/UEFI Passwords
Add another authentication layer that must be cleared before reaching the operating system or recovery environment.
3. Physical Security Controls
Restrict physical access to devices, especially in shared or public environments
Implement hardware security cables or locks for laptops
Consider tamper-evident seals for critical systems
4. Monitor for Indicators of Compromise
Existing FsTx structures on EFI partitions must be treated as an indicator of tampering attempts. System administrators should audit EFI partitions and System Volume Information directories for unexpected FsTx files.
5. Disable Unnecessary Recovery Options
Where operationally feasible, consider disabling or restricting access to Windows Recovery Environment on sensitive systems.
Implications for Compliance and Data Protection
NIS2- and DORA-relevant risk analyses often treat BitLocker as a sufficient protective measure. YellowKey forces a fresh assessment, especially for mobile endpoints.
Organizations must now reconsider:
Data breach notification requirements: After device loss, it can no longer be automatically assumed that the data is inaccessible. Notification obligations under GDPR Art. 33 must be actively reviewed
Encryption standards: Relying solely on BitLocker may not meet regulatory requirements for protecting sensitive data
Incident response procedures: Lost or stolen devices must be treated as confirmed data breaches until proven otherwise
The Path Forward
The YellowKey vulnerability represents a fundamental challenge to the assumption that hardware-backed encryption provides adequate protection for lost or stolen devices. The combination of its technical severity, ease of exploitation, and the researcher's claims about potential backdoors raises serious questions about the trustworthiness of Microsoft's security architecture.
Public zero-day releases always change the risk equation because they shrink the window between discovery and exploitation. With exploit code publicly available on GitHub and multiple researchers confirming it works, the window for malicious exploitation is wide open.
Organizations cannot wait for Microsoft to act. The time to re-evaluate BitLocker configurations, implement additional security controls, and revise risk assessments is now.
Looking Ahead
The researcher has made clear that more disclosures are coming. The anonymous researcher threatens to release further and more severe exploits, saying that the next Patch Tuesday will be "a big surprise for you, Microsoft". They also warned: "Your recent actions made me take the difficult decision to drag other companies into this. Be prepared to answer questions", suggesting vulnerabilities in products beyond Microsoft may be disclosed.
Conclusion
YellowKey is more than just another security vulnerability—it's a wake-up call about the fragility of trust assumptions in modern computing. When the default encryption solution for hundreds of millions of devices can be bypassed with a USB stick and five minutes of physical access, every organization must reassess their security posture.
The convenience of TPM-only BitLocker configurations comes at too high a cost. Until Microsoft releases a comprehensive fix and provides transparent communication about the root cause, organizations must implement defense-in-depth strategies that don't rely solely on BitLocker's protection.
As one security analyst aptly summarized: "YellowKey is a stark reminder that convenience often comes at the cost of security. Relying solely on TPM for BitLocker unlocks, while user-friendly, introduces a critical vulnerability in the recovery path".
The question now is not whether your organization's BitLocker-encrypted devices are vulnerable—it's what you're going to do about it.
Update Status: As of May 15, 2026, Microsoft has not released a patch or assigned a CVE for YellowKey. This article will be updated as new information becomes available.
Disclosure Timeline:
May 12, 2026: YellowKey and GreenPlasma exploits published on GitHub
May 13-14, 2026: Multiple independent researchers confirm exploits work
May 15, 2026: Microsoft provides standard statement but no patch or CVE assignment
#YellowKey #BitLocker #Windows11 #CyberSecurity #ZeroDay #ZeroDayExploit #WindowsSecurity #DataSecurity #InfoSec #CyberAttack #Vulnerability #Microsoft #BitLockerBypass #TPM #Encryption #EthicalHacking #SecurityResearch #InfosecNews #CyberThreat #WindowsExploit #Hackers #SecurityAlert #TechNews #DigitalSecurity #CyberDefense #EndpointSecurity #DataProtection #WinRE #CyberAwareness #TechCommunity