
The last six months were crazy but at the end I finished working in two independent projects;
1- Sigma Watch (sigmawatch.live)
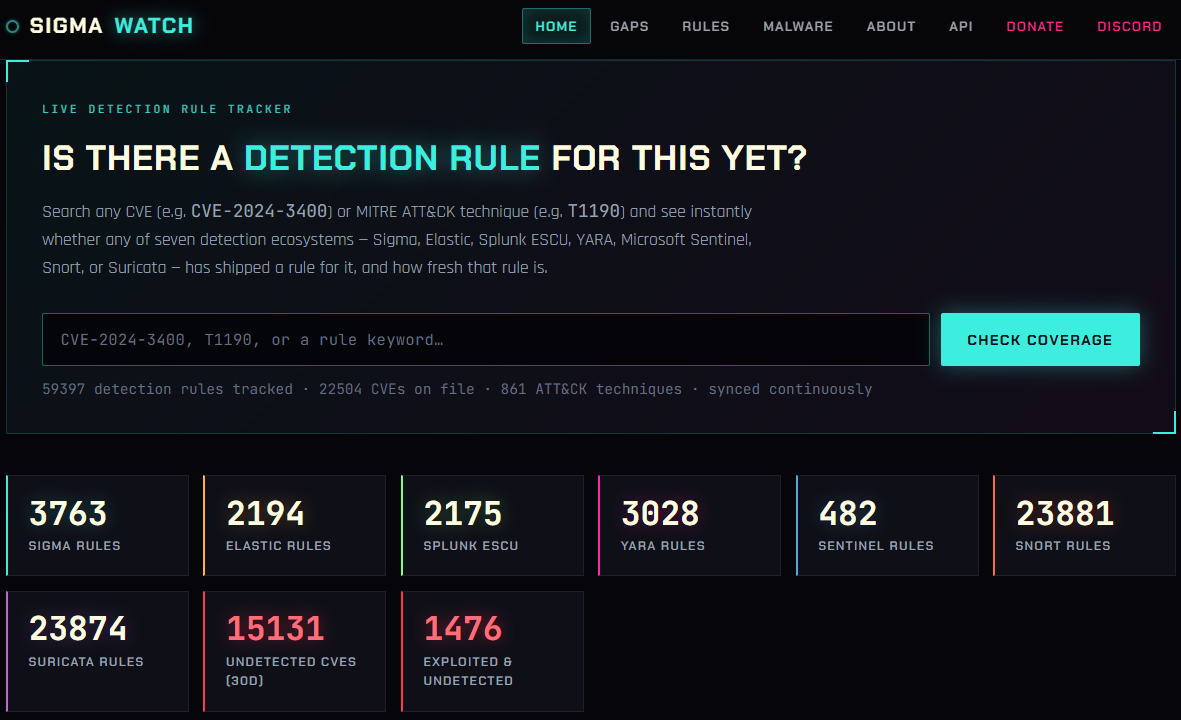 Basically every time a new CVE drops, you can find out if there is a detection for this yet. Answering that usually means searching rule repos one by one. Sigma Watch tracks thousands of open detection rules across seven sources (Sigma, Splunk, Elastic, Sentinel, YARA, Snort, Suricata). It cross-references them against recent CVEs, CISA KEV, and MITRE ATT&CK.. It also tracks well-known RATs, ransomware, and infostealers against the same rule set. Its a fast starting point for detection engineers and SOC analysts.
2- Cert Atlas (cybercert.live)
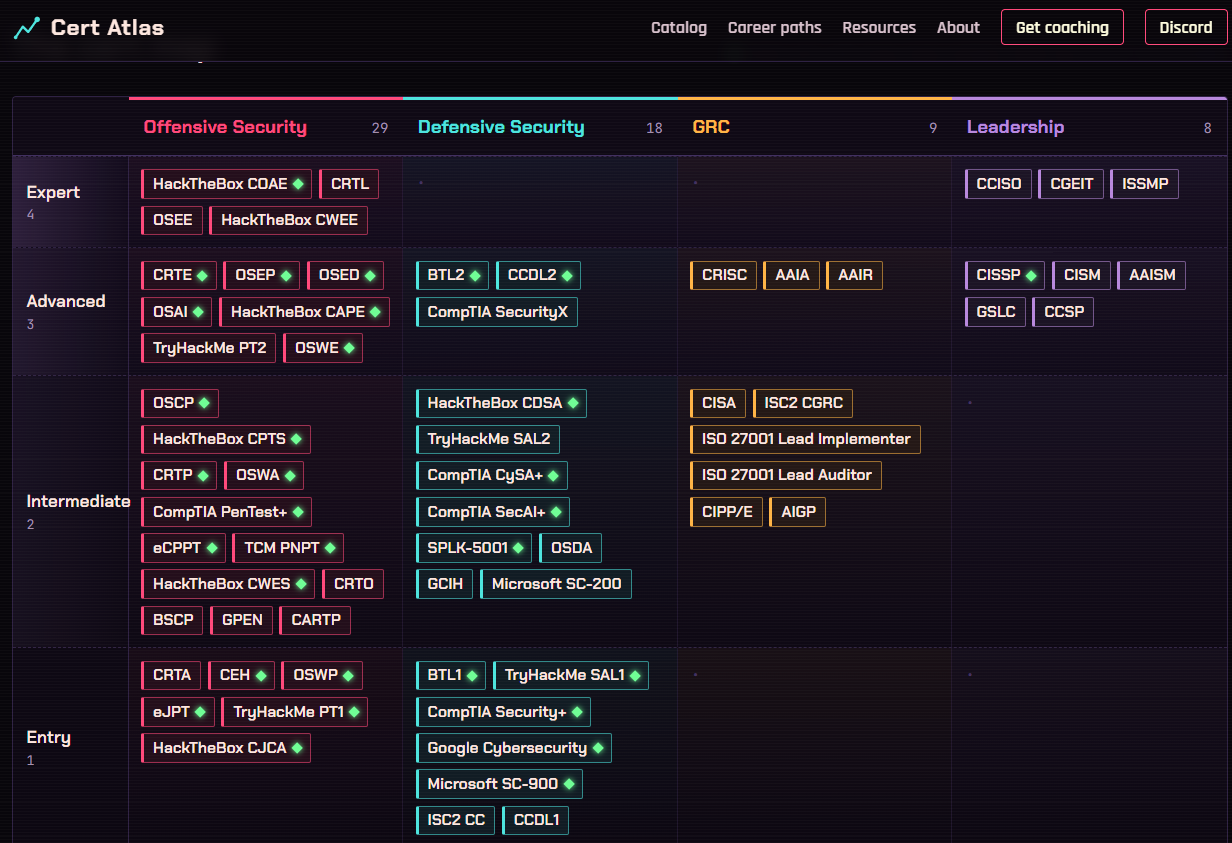 This one took me nearly two months just to create the draft 😅 so basically the idea is choosing a certification shouldnt feel like guesswork.
Cert Atlas organizes cybersecurity certifications by track and level, so beginners can see where to start and experienced professionals can see what comes next.
Both are free and built from scratch. If you work in a SOC, do detection engineering, or are planning your next cert, Id love your feedback.
Whats missing? Let me know
#CyberSecurity #DetectionEngineering #SOC #BlueTeam #InfoSec #CyberCareers