

Shiba is a newly emerged cyber extortion and ransomware group that surfaced around September 2026.
 Hi, thanks for taking the time to speak with Inside Darknet. For people who don't know you yet, who is Shiba, and why did you choose that name?
We chose the name for our love of shiba dogs. It is as simple as that haha.
You are a relatively new group, emerging in September 2026. Is this your first project, or had you operated before?
We are adverts from older projects but with the goal of maximizing extortion, many groups still believe leaking big bloated zip archives that cannot even be downloaded over tor is harmful and serves as some form of deterrent to further victims, it is simply not the case, we will discuss this further later on in the interview.
How did you first get into hacking?
We simply got into pentesting from years of work, and we continue to work with various cases and advertisers ;
What happens to an organization you attack? Do you encrypt its files, steal information and threaten to publish it, or both?
Yes, we have a strong emphasis for encryption in particular, the idea that data serves as the main driving point for a ransom payment is simply not true. So encryption for advertisers within our program is really encouraged.
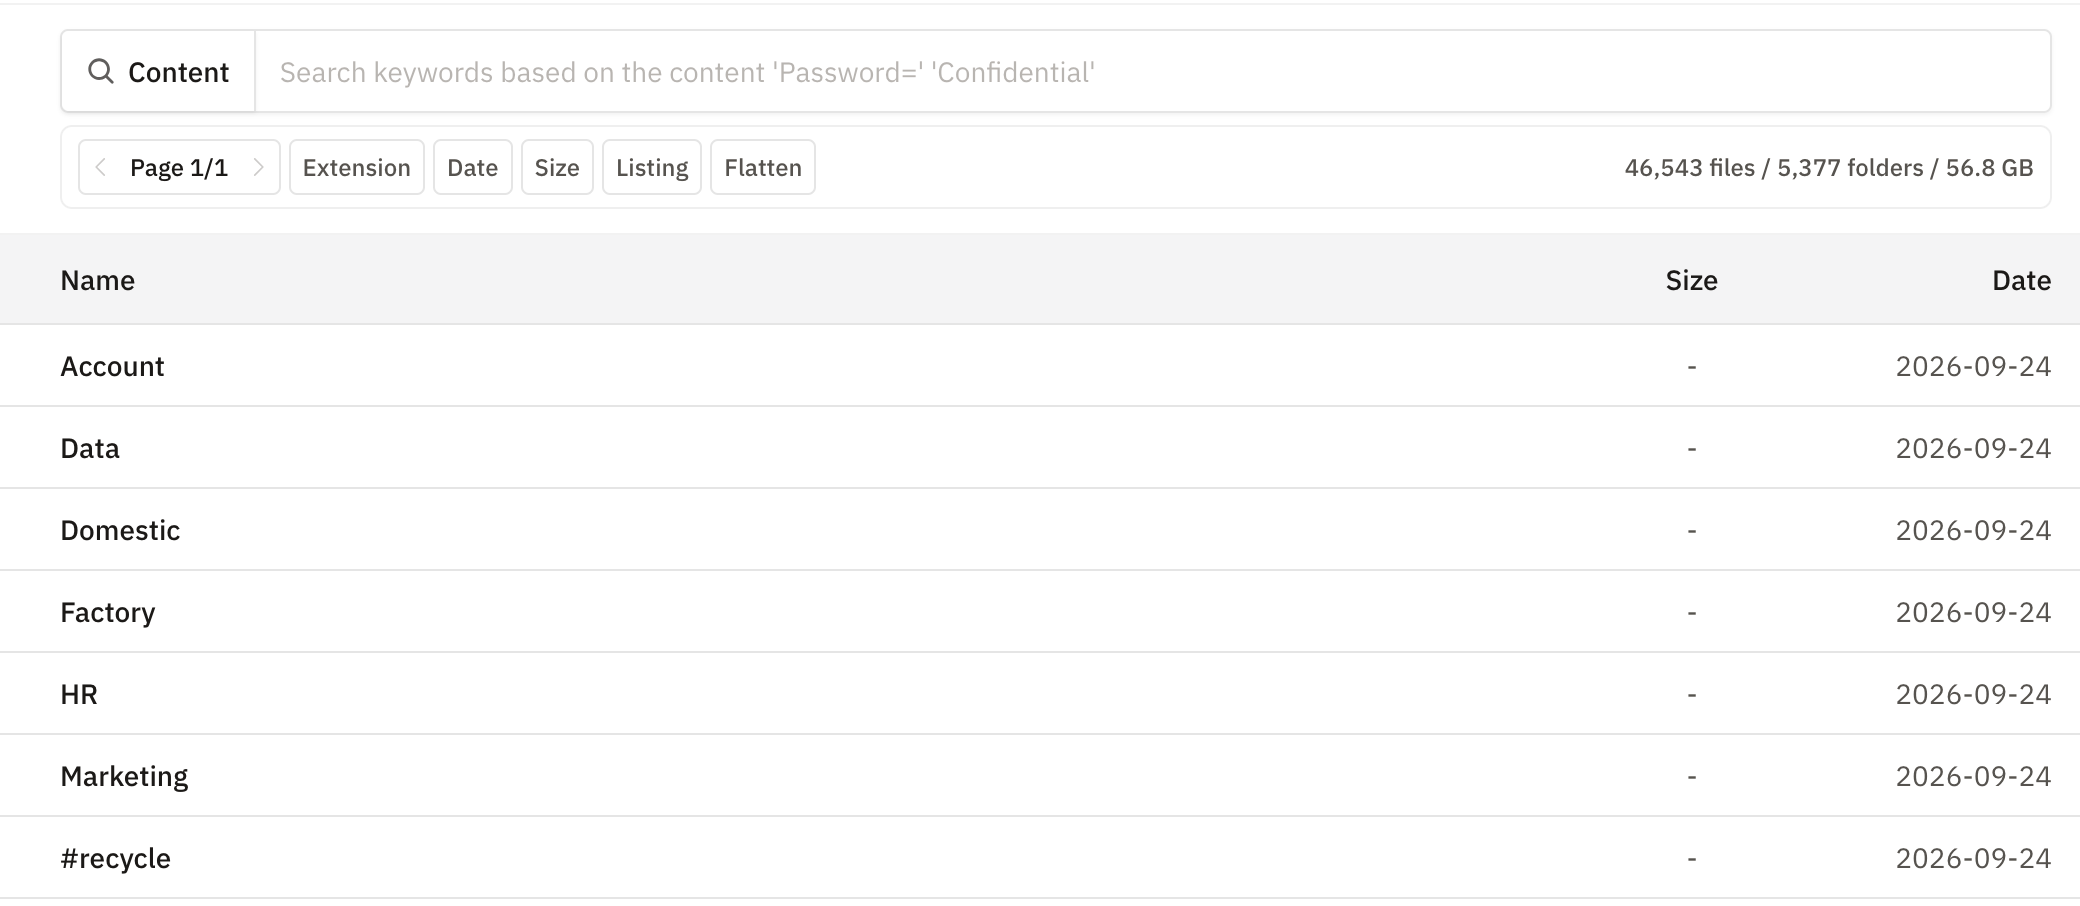
For those who do not want to make a deal, the data is indexed then published, it can be searched for within 3 main tags on our leak site.
File name keywords: you can search for key words and the corresponding key words that are the files names appear
Content: you can search for content within an extremely large selection of files types, for example Sensitive or Confidential and all files with that word in it will appear with a short snippet showing where it came from. It is hard to explain, check out our leak site hxxp://shibaitobajtr6yctvrijfitnugfulkmprrqbmu2ysk3zyzx2ufe3yqd[.]onion and it will make more sense.
Sensitive: You can search for hardcoded regex of sensitive data types, such as SSN and it will find all SSNs within the publicated files, medicare numbers, passport numbers, drivers license numbers and more. It is also for the sensitive specific to the victim companies country, so take Germany for example. If it was a german company it is the german equivalent of a USA SSN, you get the idea.
 Do you develop your own ransomware?
Yes, all our software is completely made from scratch. There is no binary that is compiled with us with any shitty leftovers from leaked source code.
Our software is particularly designed to prevent file carving, when incident responders try to recover files for their clients with a ESXI hypervisor, they will often try to find the unencrypted sections, our software is designed to allow for intermittent encryption but loads of strips equally spread out across the encrypted VM/file so that it is impossible to get for example critical active directory files back. (and the only option is to pay for a decryptor)
Let's say an organisation gets hacked by you. They then restore everything through backups and refuse to pay - what happens next?
As previously covered it is published in the most harmful way, and we have great connections with people in the media. They are definitely not shy to post stories of the victim company to harm them as much as possible.
Our data exposing team will bury companies very easily with global media watching.
And if they pay - what happens next?
They pay and the deal is secret, we have seen as a result of our leak site design, (and our features) a very encouraging payment rate relative to our total victims for this partner program.
A company cannot easily verify that every copy of its stolen data has been deleted. Why should it trust you or anyone working with you to keep that promise?
If data was leaked again after a company paid us, then no other company in the future would pay us. There is zero reason for anybody to not follow through on their wish. We are not teenagers haha.
Your listings also include Friendly Senior Living and Antwerp House Dentistry. What boundaries do you have around healthcare, elderly people and children?
No, we have zero bounderies. They are used in the future as deterrents to future companies, healthcare, children anything can and will be attacked. Limiting yourself to only some sectors is not how the ransomware ecosystem works and we do not follow on this. Adverts in our program do not like being limited and will simply take their access over to another program that allows it.
What do you think about the current state of cybersecurity?
The current state of cyber security is why groups similar and like us flourish so well, it is this naive assumption that companies can be secure by retaining a multi-million dollar cyber security firm that does not help them at all, anyone can and will be attacked given the chance))
There's more and more Threat Actors fully relying on AI, or developing their tooling with it. How much has AI changed the way you work?
We do not use AI for anything, the reality with these tools is the FBI and other agencies have access to these tools, there is simply no need to use AI. I do not know a single advertiser that works with us that uses any AI.