

CVE-2026-31431 ("Copy Fail") dropped as a 0-day — disclosed with working exploits before distro maintainers even had patches ready. Local privilege escalation, container escape, affects every kernel from 4.14 to 6.18.21.
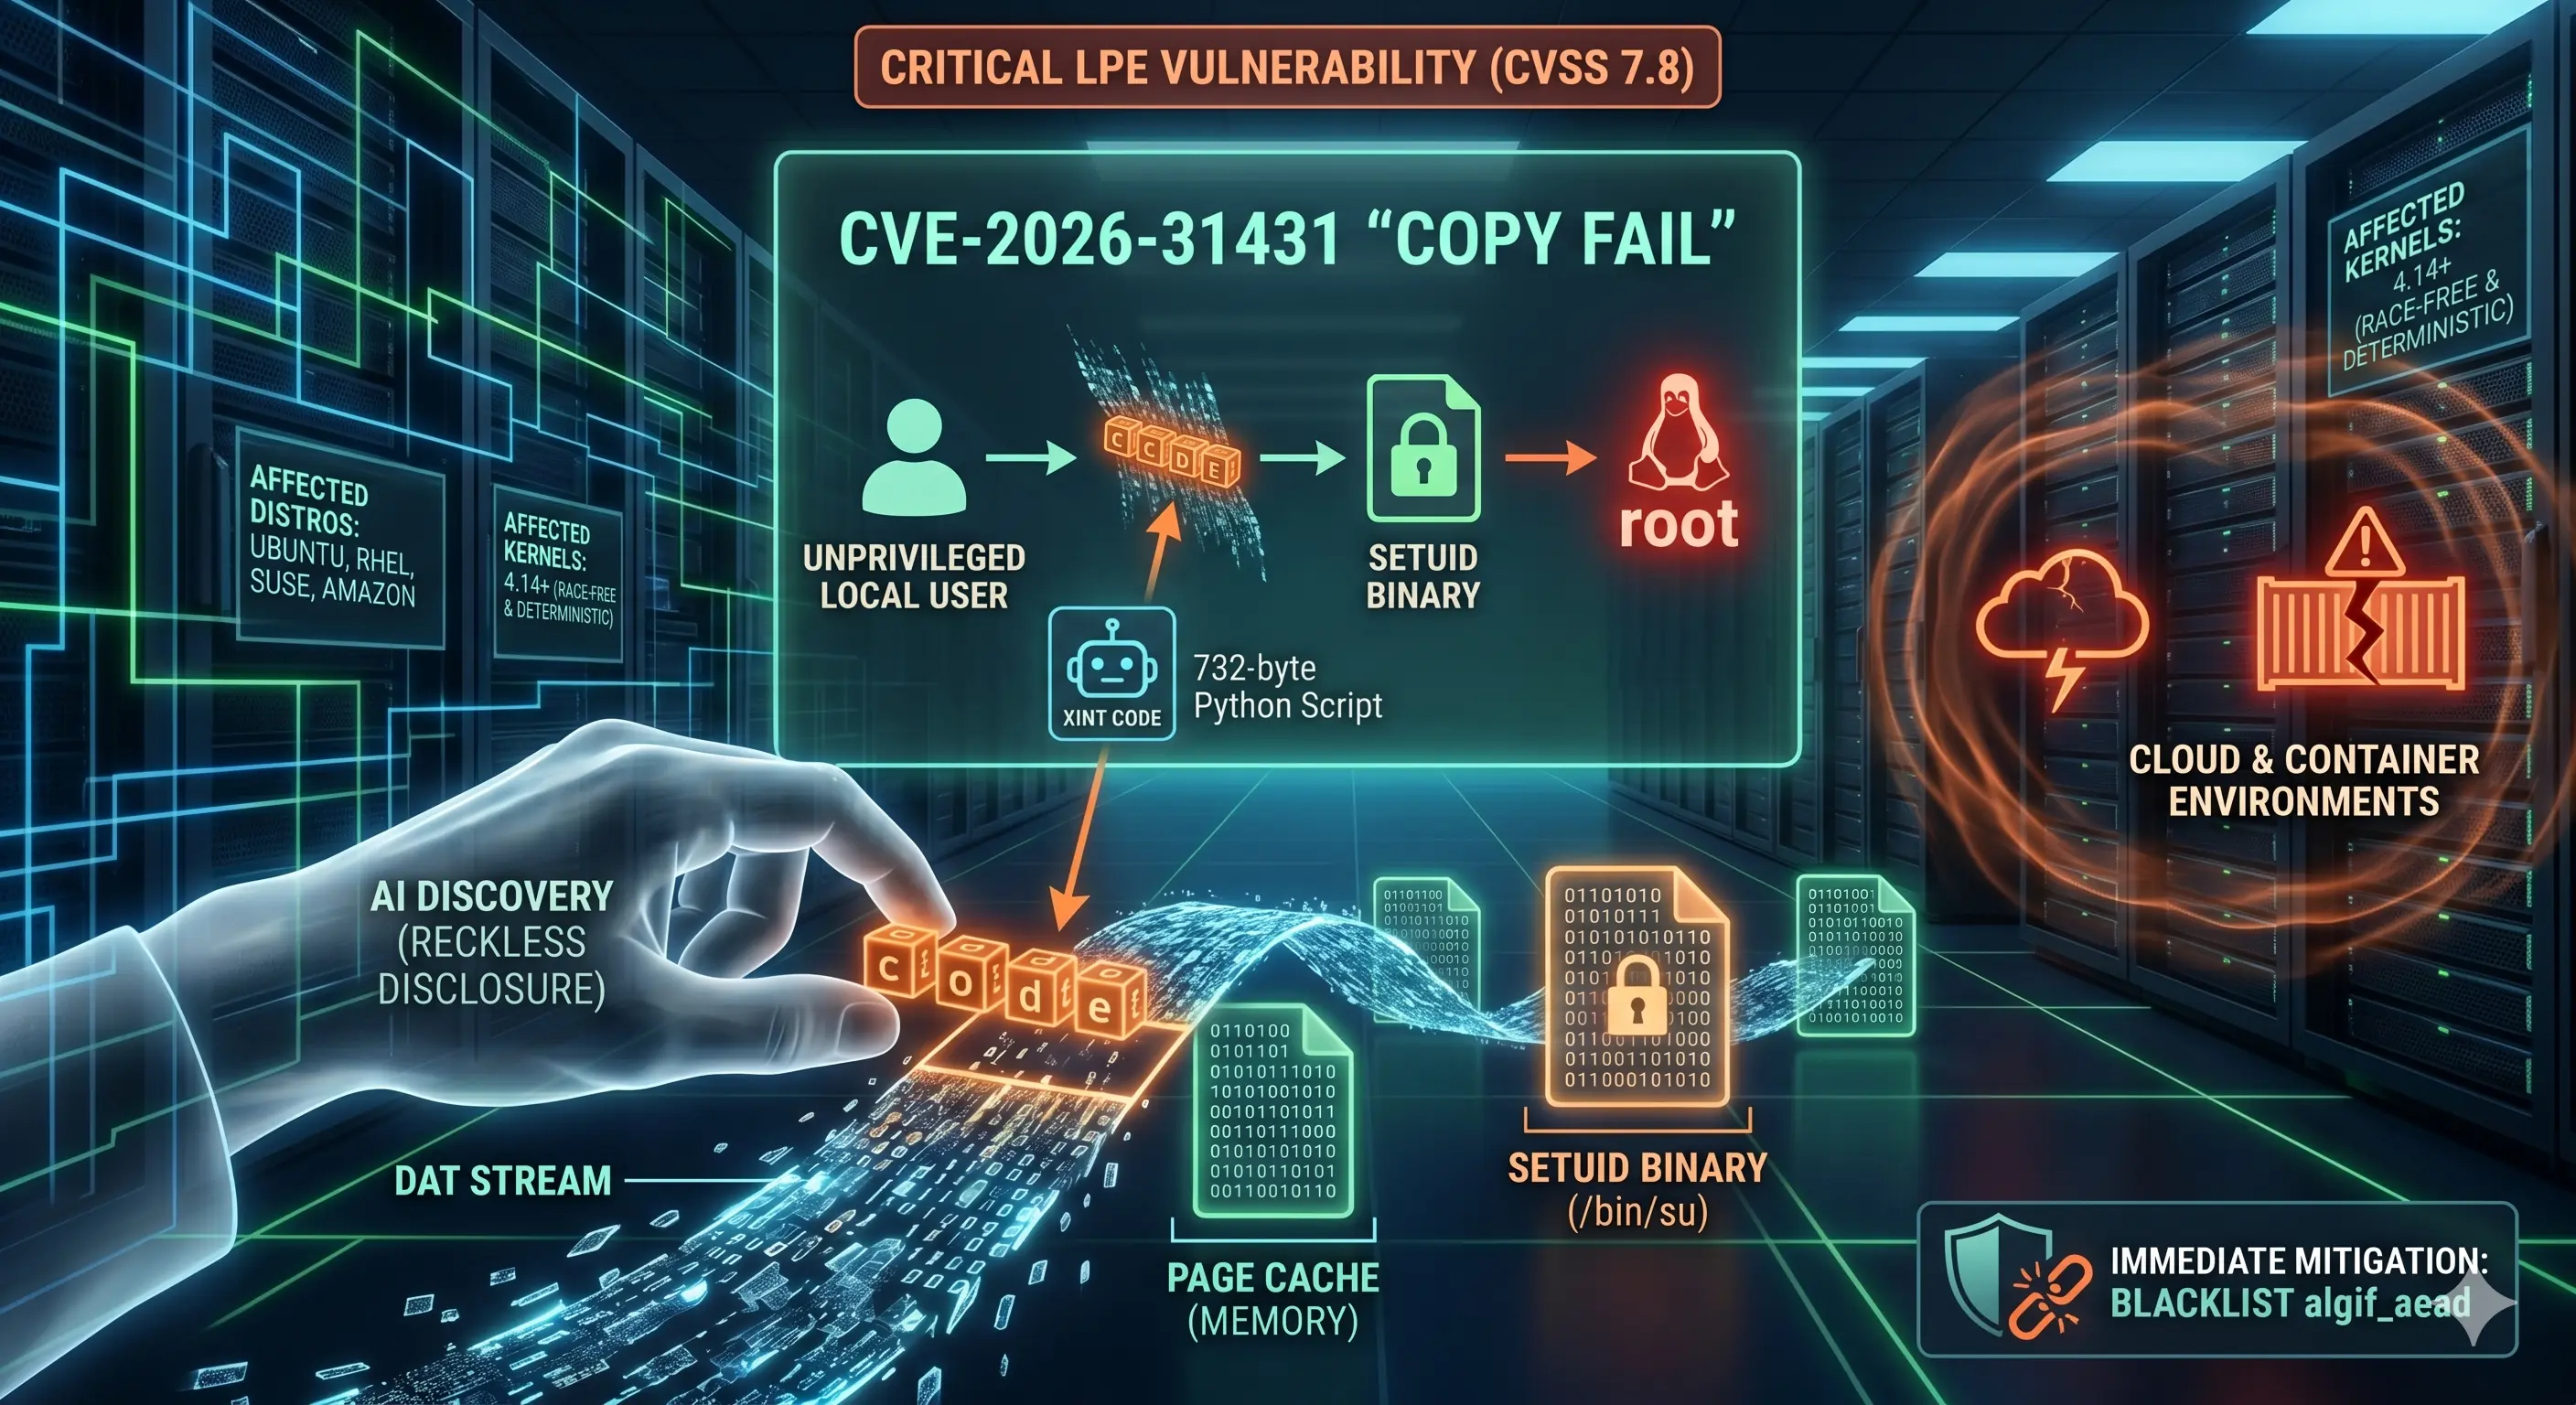 If you run Linux servers, containers, CI runners, or a VPS with SSH access: you're affected.
I wrote a hands-on guide covering the full response:
→ Check if your kernel is vulnerable (interactive checker on the page)
→ Blacklist the exploited module immediately — two commands
→ Verify whether your distro has a patch available yet
→ Apply the patch and reboot safely
No paywalls, no signup, no fluff. Just the commands.
Read it here: https://hardcore.engineer/articles/copy-fail-cve-2026-31431-patch-and-automate