
Data allows firms categorized as financial services to improve capabilities derived from information technology (Valencia, Mugge, Schoormans, & Schiffersteinm, 2015; Lim, Kim, Kim, Heo, Kim, & Maglio, 2018). Capabilities to use data require understanding where knowledge can be obtained across the technology infrastructure and what insights are essential to inform the cybersecurity risk decision-making process (Ani, He, & Tiwari, 2019; Janković, Adrodegari, Saccani, & Simeunović, 2022). Determining requisite capabilities to better use insights from applications and supporting infrastructure is fundamental to developing innovative strategies that protect this segment of the financial sector (Janković et al., 2022).
Although these organizations have the technology to deliver financial services, the extent to which data is used to manage critical applications has not been explored (Cybersecurity and Infrastructure Security Agency (CISA), 2015; Securities Industry and Financial Markets Association (SIFMA), 2022c). These unexplored areas include misunderstanding information technology operational costs, technology use optimization, and cybersecurity risks to current products and services (CISA 2015; SIFMA, 2022abc). Exploring this understudied problem helps financial service organizations and stakeholders increase digital servitization, efficiency, and resiliency to cyber-attacks (CISA, 2015; Valencia et al., 2015; Lim et al., 2018; Cyber Risk Institute, 2022; Janković et al., 2022).
The Proposed Framework
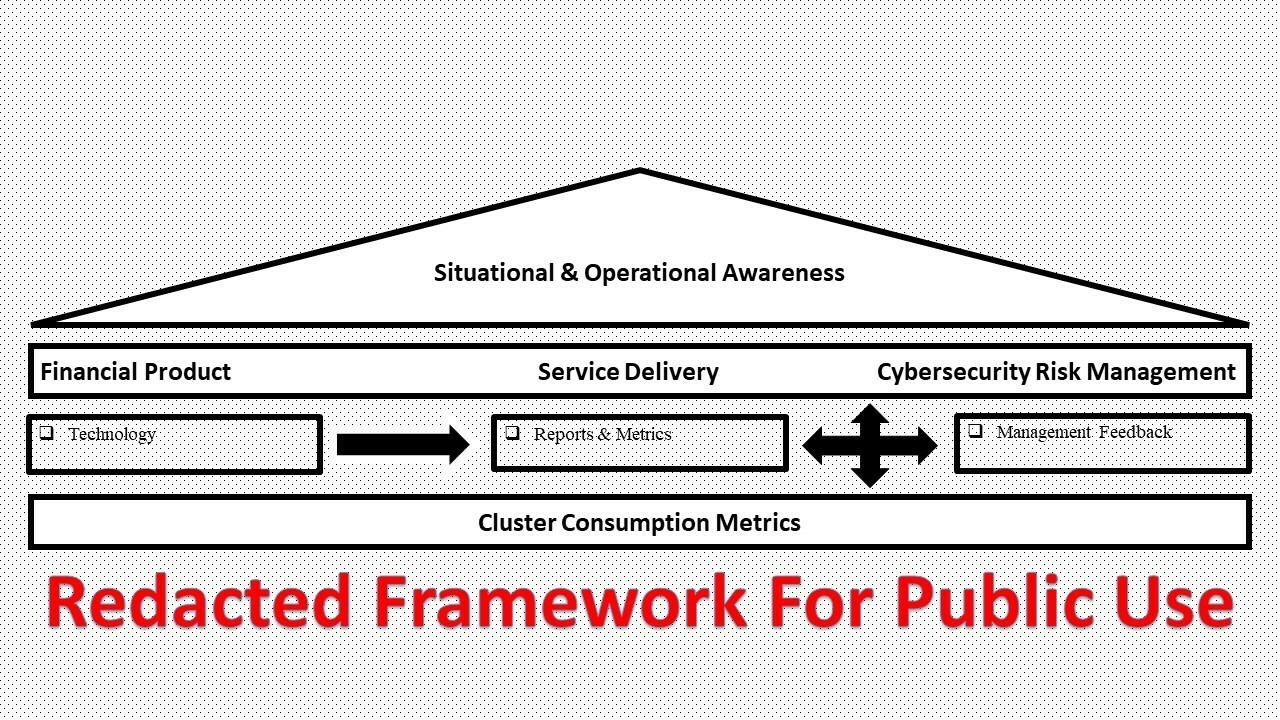
Financial services agencies have not explored data to manage critical applications and associated technology operational costs (Valencia et al., 2018). This unexplored data can help provide strategic, tactical, and operational decision-making to increase efficiency and resilience to cyber-attacks (CISA, 2015; Cyber Risk Institute, 2022; SIFMA, 2022abc). The proposed framework will benefit financial technology-intensive organizations by providing advanced awareness for product and service delivery and cybersecurity risk management. The framework will update management scorecards with infrastructure product catalogs sourced from accounting ledgers and replacement costs sourced from supplier product catalogs (SABSA, 2020).
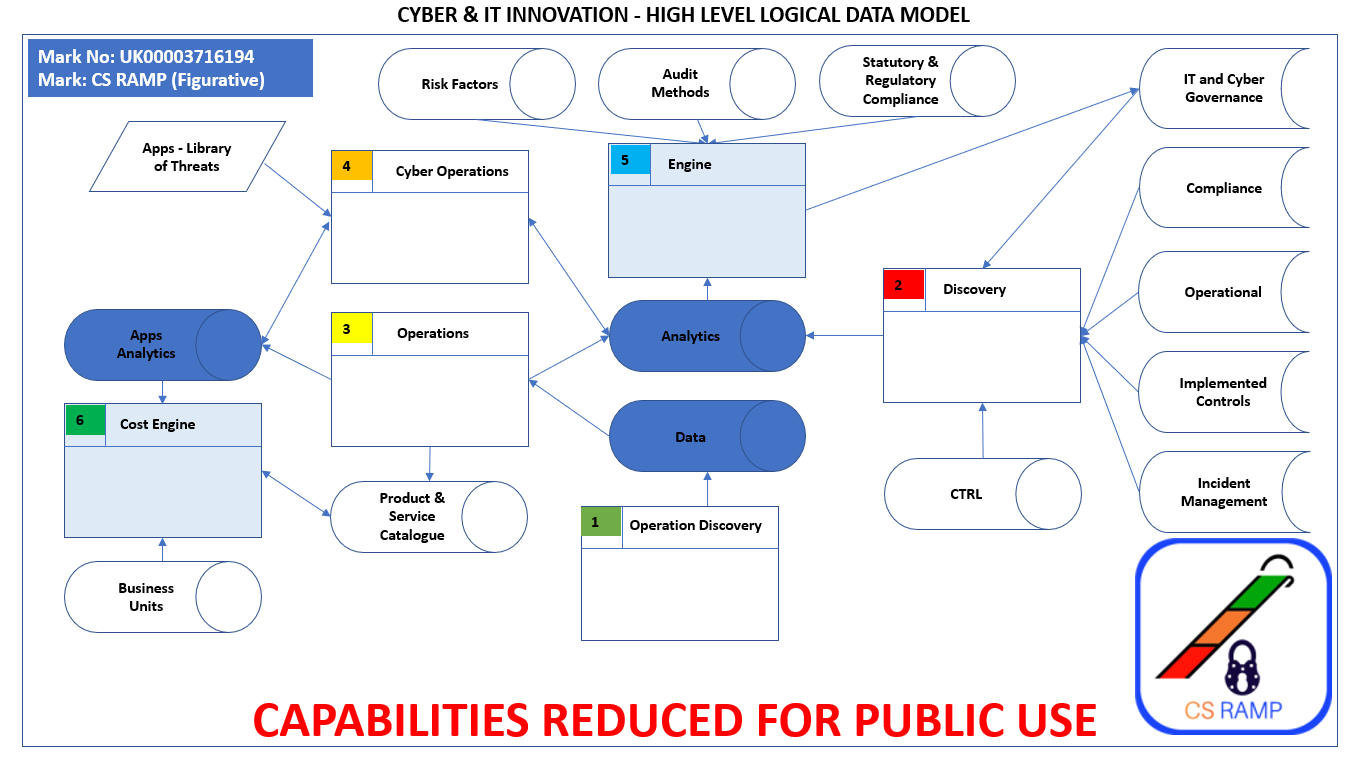
Other application costs, such as data center occupancy, direct labor and expenses, and overheads will be sourced from the accounting and management information systems (SABSA, 2020). In addition, cybersecurity risk domain data will originate from implemented controls, such as incident management. The Cyber Resilience Review (CRR) and Federal Financial Institutions Examination Council (FFIEC) risk assessment techniques serve as references to service continuity management (Department of Homeland Security & Carnegie Mellon University; 2016b; Federal Financial Institutions Examination Council (FFIEC), n.d.).
Capability Convergence
The purpose of this research is to deliver a practical framework that uses innovative technologies to develop an integrated solution. The solution will manage critical application costs and cybersecurity risks in organizations with both significant infrastructure budgets and risk exposure to cyber-attacks. The below-redacted data model provides one of several lenses to understand how to achieve operational and situational awareness.
CS RAMP: CYBER SECURITY RISK ASSESSMENT AND MEASUREMENT PLATFORM
Application number: 10026774
Competition: Innovate UK Smart Grants: October 2021
Significance
This qualitative case study research findings will help the industry understand how financial service organizations use data to establish standards for critical application costs and cybersecurity risk management, in the delivery of products and services. This will add to the body of knowledge by helping financial sector organizations understand this segment of the sector and potentially adopt recommendations for improved data and technology structures.
The researcher will conduct this study to explore the required capabilities to use data and where knowledge can be obtained across the technology infrastructure. Thus, providing a framework for determining what insights are essential to inform financial technology and cybersecurity risk decision-making processes.
Purpose
Video: https://player.hourone.ai/2a00df6032bf404fa8592ba5cb2470f4
I am exploring options to collaborate and funding to implement this framework.
Contact Researcher
Dr. Dustin Fraser, CASP+, LCSPC, SSCP
Email: [email protected]
Research Site: https://1gcyber.com
LinkedIn: https://www.linkedin.com/in/dustinfraser/
References Available
https://www.captechu.edu/degrees-and-programs/doctoral-degrees/financial-cybersecurity-phd