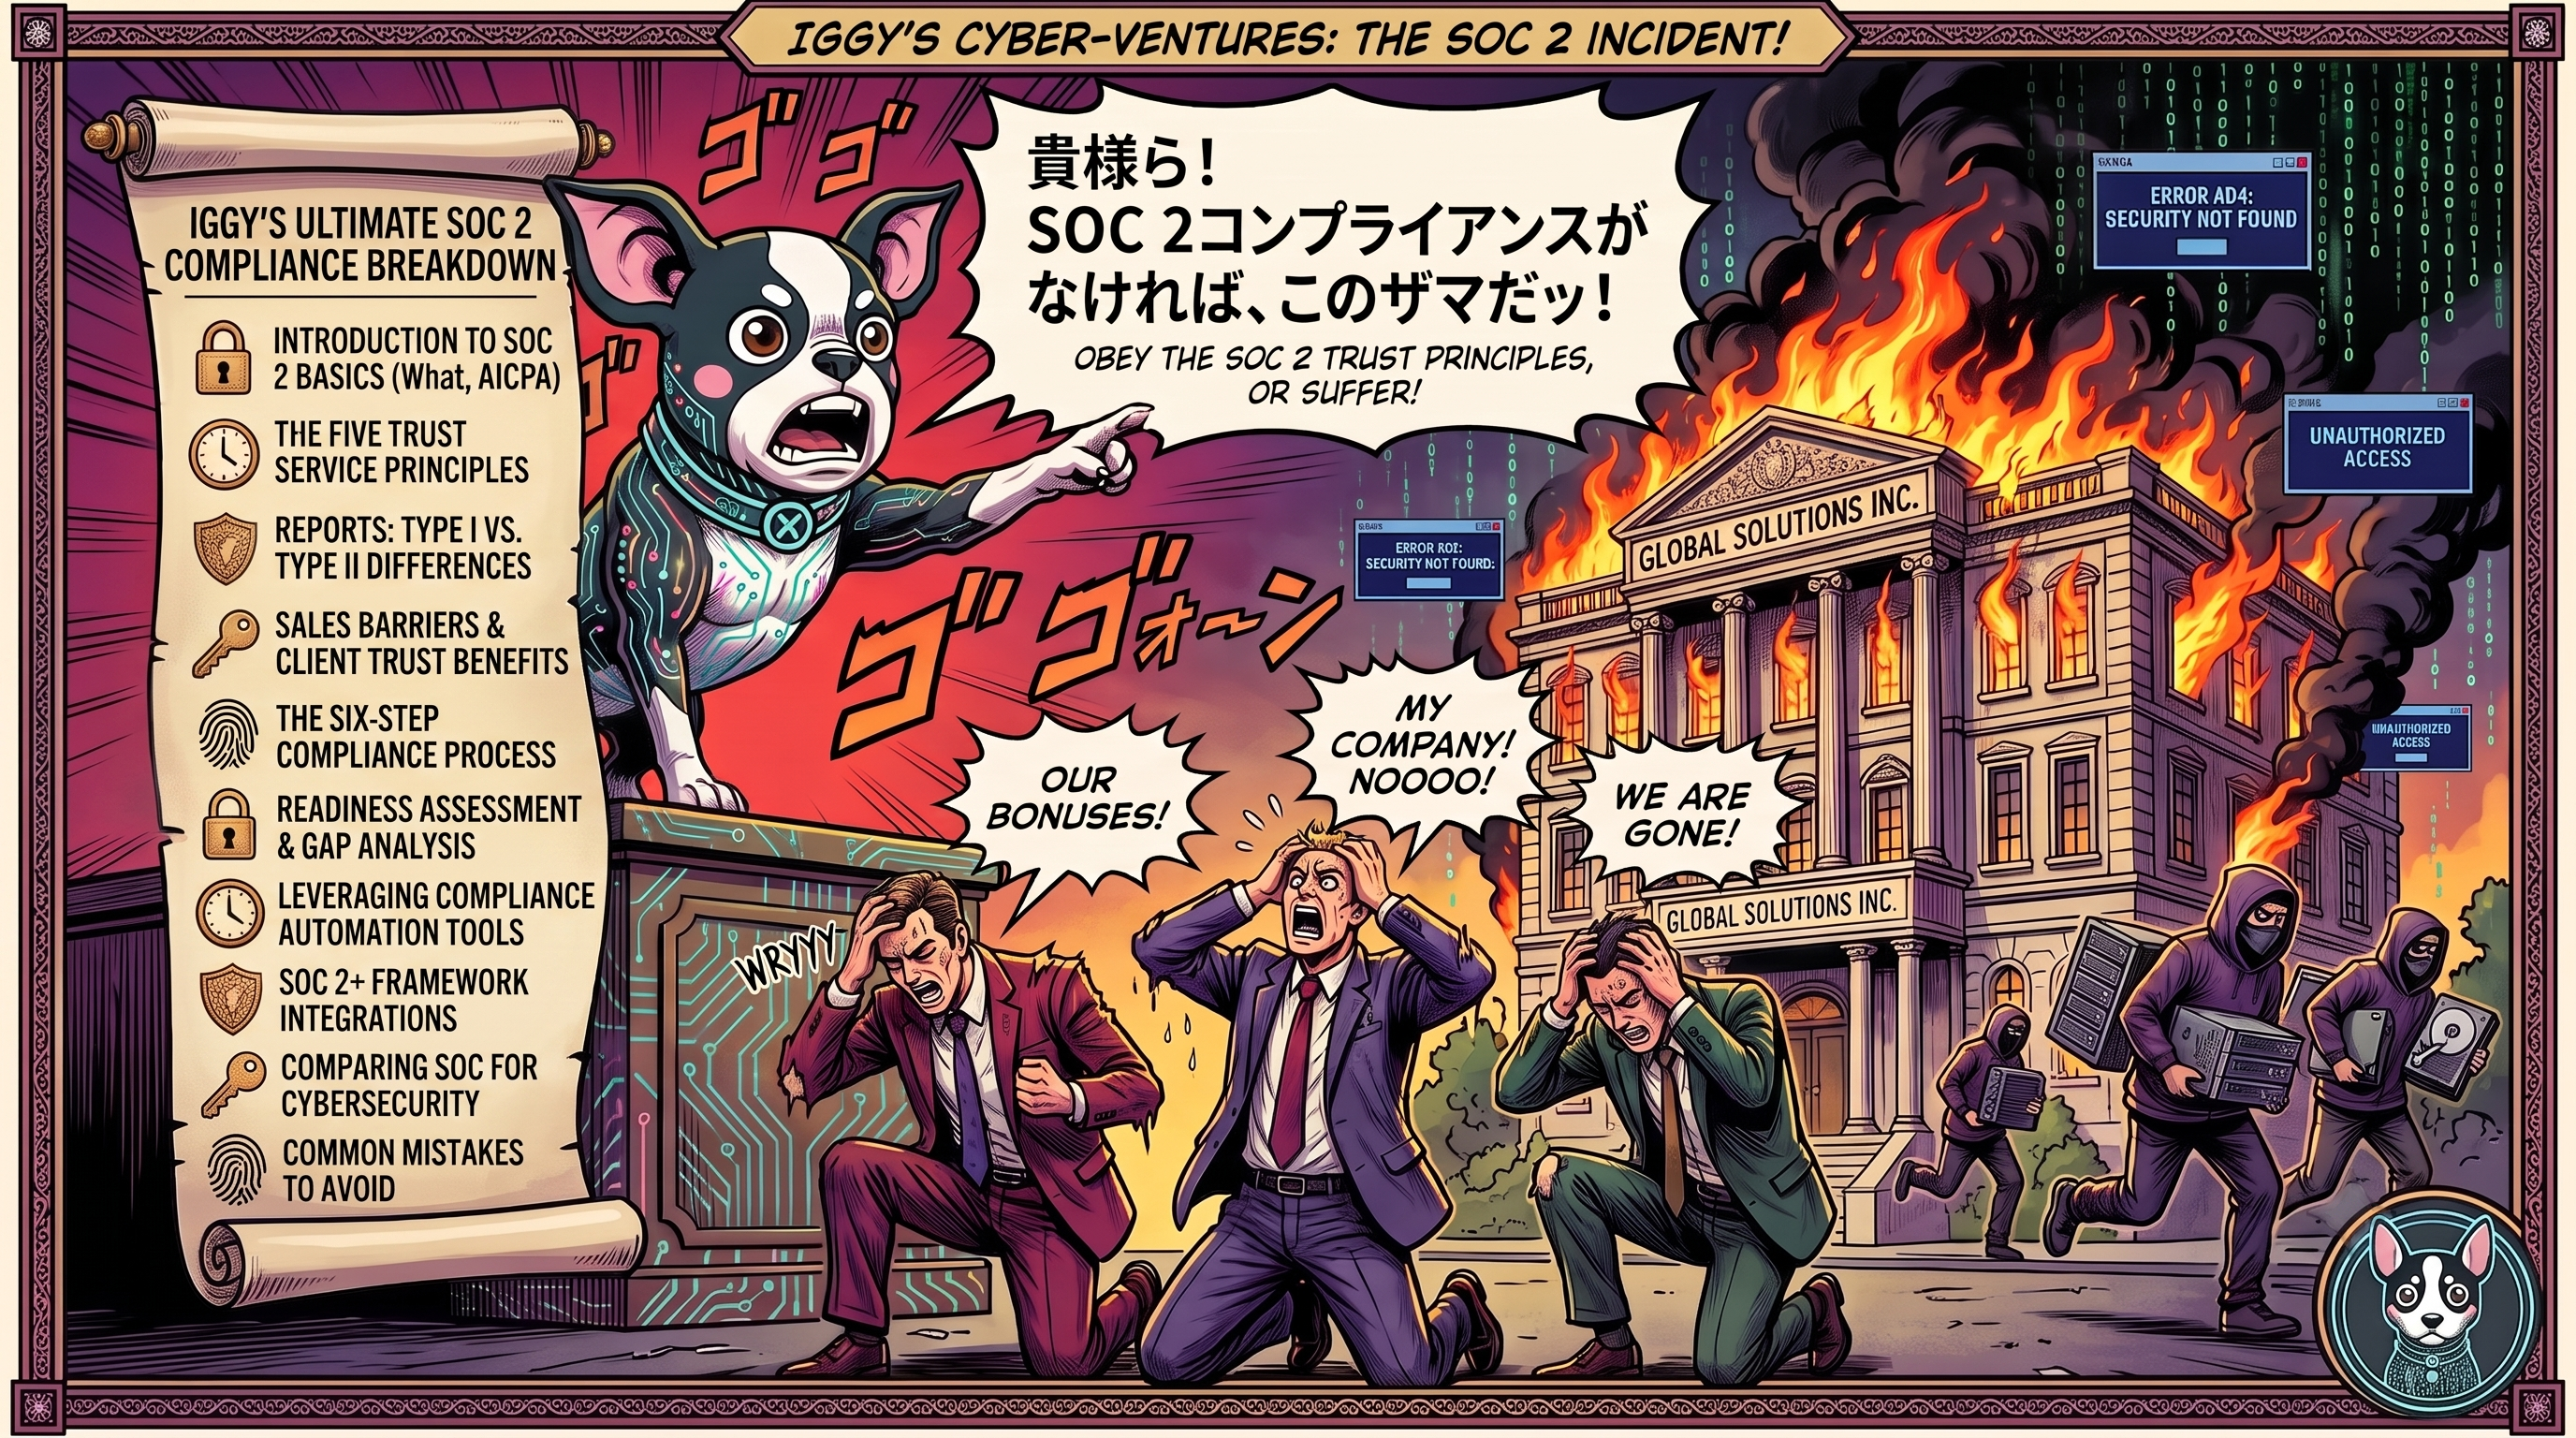

Demonstrating information security is no longer just about answering some vendor questionnaire. Lately enterprise decision makers are asking for verifiable SOC 2 reports, to check robust internal controls before they sign anything.
And to protect the bottom line and speed up the sales cycle, organizations really need to step past manual compliance tracking. I just put together a rough breakdown of how to navigate the assessment lifecycle and keep your security posture locked down. It basically comes down to integrating stronger architectural frameworks, these usually include:
🔒 Aligning with foundational Trust Service Principles like Security and Privacy to protect sensitive data.
⏱️ Upgrading from a basic Type I snapshot to a rigorous Type II report to prove operational efficacy over an extended duration.
📊 Deploying compliance automation platforms to centralize evidence collection and eliminate administrative fatigue.
☁️ Customizing specific controls to safeguard massive operations, including Azure and Microsoft 365 environments supporting over eight hundred users and a hundred workstations.
You can no longer just trust a verbal promise of security or a static policy document anymore.
Read more in the newly posted article outlining how to upgrade your compliance strategy here: https://www.cybercritters.net/article.html?id=article-1786028679859
#SOC2 #CyberSecurity #InformationSecurity #CloudSecurity #TechLeadership #ComplianceManagement